

Privacy Policy
Table of Contents
- Introduction and Overview
- Scope of Application
- Legal Basis
- Contact Information for the Data Controller
- Contact Information for the Data Protection Officer
- Retention period
- Rights Under the General Data Protection Regulation
- Data Transfer to Third Countries
- Data Processing Security
- Communication
- Data Processing Agreement (DPA)
- Cookies
- Application Information
- Customer Data
- Registration
- Web Hosting Introduction
- Introduction to Web Analytics
- Email Marketing Introduction
- Social Media Introduction
- Cloud Services
- Online Map Services: Introduction
- Miscellaneous: Introduction
- Explanation of Terms Used
Introduction and Overview
We have prepared this Privacy Policy (Version 09/27/2023-122077330) to explain to you, in accordance with the provisions of the General Data Protection Regulation (EU) 2016/679 and applicable national laws, which personal data (hereinafter “data”) we, as the data controller—and the data processors we engage (e.g., service providers)—process, will process in the future, and what legal rights you have. The terms used are to be understood as gender-neutral.
In short: We provide you with comprehensive information about the data we process about you.
Privacy policies usually sound very technical and use legal jargon. This privacy policy, however, is intended to explain the most important points to you as simply and transparently as possible. Where it promotes transparency, technical terms are explained in a reader-friendly manner, links to further information are provided, and graphics are used. We use clear and simple language to explain that, in the course of our business activities, we process personal data only when there is a corresponding legal basis for doing so. This certainly isn’t possible if we provide explanations that are as brief, unclear, and legally technical as those often found online when it comes to data protection. I hope you find the following explanations interesting and informative, and perhaps you’ll discover a piece of information or two that you weren’t aware of before.
If you still have questions, please contact the responsible party listed below or in the legal notice, follow the provided links, and review additional information on third-party websites. You can, of course, also find our contact information in the legal notice.
Scope of Application
This Privacy Policy applies to all personal data processed by us within the company and to all personal data processed by companies we have commissioned (data processors). By “personal data,” we mean information as defined in Article 4(1) of the GDPR, such as a person’s name, email address, and mailing address. The processing of personal data enables us to offer and bill for our services and products, whether online or offline. The scope of this Privacy Policy includes:
- All online platforms (websites, online stores) that we operate
- Social Media Presence and Email Communication
- Mobile apps for smartphones and other devices
In short: This Privacy Policy applies to all areas in which personal data is processed in a structured manner within the company through the channels mentioned. Should we enter into a legal relationship with you outside of these channels, we will inform you separately if necessary.
Legal Basis
In the following Privacy Policy, we provide you with transparent information regarding the legal principles and regulations—that is, the legal basis under the General Data Protection Regulation—that allow us to process personal data.
With regard to EU law, we refer to REGULATION (EU) 2016/679 OF THE EUROPEAN PARLIAMENT AND OF THE COUNCIL of April 27, 2016. You can, of course, read this EU General Data Protection Regulation online on EUR-Lex, the portal for EU law, at https://eur-lex.europa.eu/legal-content/DE/ALL/?uri=celex%3A32016R0679.
We process your data only if at least one of the following conditions applies:
- Consent (Article 6(1)(a) of the GDPR): You have given us your consent to process data for a specific purpose. An example would be storing the data you entered in a contact form.
- Contract (Article 6(1)(b) of the GDPR): We process your data to fulfill a contract or pre-contractual obligations with you. For example, when we enter into a purchase agreement with you, we need certain personal information in advance.
- Legal Obligation (Article 6(1)(c) of the GDPR): We process your data when we are subject to a legal obligation. For example, we are legally required to retain invoices for accounting purposes. These invoices typically contain personal data.
- Legitimate Interests (Article 6(1)(f) of the GDPR): In cases where legitimate interests do not infringe upon your fundamental rights, we reserve the right to process personal data. For example, we must process certain data in order to operate our website securely and cost-effectively. This processing therefore constitutes a legitimate interest.
Other conditions, such as the collection of data in the public interest, the exercise of public authority, and the protection of vital interests, generally do not apply to us. However, should such a legal basis be applicable, it will be indicated in the appropriate section.
In addition to the EU regulation, national laws also apply:
- In Austria, this is the Federal Act on the Protection of Natural Persons with Regard to the Processing of Personal Data (Data Protection Act), or DSG for short.
- In Germany, the Federal Data Protection Act( BDSG) applies.
If any additional regional or national laws apply, we will provide you with information about them in the following sections.
Contact Information for the Data Controller
If you have any questions regarding data protection or the processing of personal data, please find the contact information for the responsible person or department below:
Langer GmbH
Steyrerstrasse 13, 4470 Enns
Austria
Authorized Representative: Fritz Aichhorn
Email: fritz@langer-magnet.com
Phone: +43 7223 82592-0
Legal Notice: https://www.langer-magnet.com/impressum/
Contact Information for the Data Protection Officer
Below are the contact details for the Data Protection Officer:
Langer GmbH
Fritz Aichhorn
Steyrerstrasse 13, 4470 Enns
Austria
Email: fritz@langer-magnet.com
Phone: +43 664 2324180
Retention period
It is our general policy to retain personal data only for as long as is strictly necessary to provide our services and products. This means that we delete personal data as soon as the reason for processing it no longer exists. In some cases, we are legally required to retain certain data even after the original purpose has ceased to exist, for example, for accounting purposes.
If you wish to have your data deleted or wish to revoke your consent to data processing, the data will be deleted as soon as possible, provided there is no legal obligation to retain it.
We will provide you with information below regarding the specific duration of each data processing activity, provided we have further details on this matter.
Rights Under the General Data Protection Regulation
In accordance with Articles 13 and 14 of the GDPR, we are informing you of the following rights to which you are entitled to ensure that your data is processed in a fair and transparent manner:
- Under Article 15 of the GDPR, you have the right to know whether we process any of your personal data. If we do, you have the right to receive a copy of that data and to be provided with the following information:
- the purpose for which we process the data;
- the categories—that is, the types of data—that are processed;
- who receives this data, and if the data is transferred to third countries, how security can be guaranteed;
- how long the data is stored;
- the existence of the right to rectification, erasure, or restriction of processing, and the right to object to processing;
- that you can file a complaint with a supervisory authority (links to these authorities are provided below);
- the source of the data, if we did not collect it from you;
- whether profiling is being carried out—that is, whether data is being automatically analyzed to create a personal profile of you.
- Under Article 16 of the GDPR, you have the right to have your data corrected, which means that we must correct any data if you find any errors.
- Under Article 17 of the GDPR, you have the right to erasure (“right to be forgotten”), which specifically means that you may request the erasure of your data.
- Under Article 18 of the GDPR, you have the right to restrict processing, which means that we may only store the data but may not continue to use it.
- Under Article 20 of the GDPR, you have the right to data portability, which means that, upon request, we will provide you with your data in a commonly used format.
- Under Article 21 of the GDPR, you have the right to object, which, once exercised, will result in a change to the processing.
- If the processing of your data is based on Article 6(1)(e) (public interest, exercise of official authority) or Article 6(1)(f) (legitimate interest), you may object to the processing. We will then review as soon as possible whether we can legally comply with this objection.
- If your data is used for direct marketing purposes, you may object to this type of data processing at any time. After that, we may no longer use your data for direct marketing.
- If data is used for profiling, you may object to this type of data processing at any time. We may no longer use your data for profiling after that.
- Under certain circumstances, pursuant to Article 22 of the GDPR, you have the right not to be subject to a decision based solely on automated processing (such as profiling).
- Under Article 77 of the GDPR, you have the right to lodge a complaint. This means that you may file a complaint with the data protection authority at any time if you believe that the processing of personal data violates the GDPR.
In short: You have rights—don’t hesitate to contact the responsible party listed above!
If you believe that the processing of your data violates data protection law or that your data protection rights have been infringed upon in any other way, you may file a complaint with the supervisory authority. In Austria, this is the Data Protection Authority, whose website can be found at https://www.dsb.gv.at/. In Germany, there is a data protection commissioner for each federal state. For more information, you can contact the Federal Commissioner for Data Protection and Freedom of Information (BfDI). The following local data protection authority has jurisdiction over our company:
Austrian Data Protection Authority
Director: Mag . Dr. Andrea Jelinek
Address: Barichgasse 40-42, 1030 Vienna
Phone: +43 1 52 152-0
Email: dsb@dsb.gv.at
Website: https://www.dsb.gv.at/
Data Transfer to Third Countries
We transfer or process data to countries outside the EU (third countries) only if you consent to such processing, if it is required by law, or if it is contractually necessary—and in any case, only to the extent generally permitted. In most cases, your consent is the primary reason we process data in third countries. The processing of personal data in third countries such as the United States—where many software providers offer services and have their server locations—may mean that personal data is processed and stored in unexpected ways.
We expressly point out that, in the opinion of the European Court of Justice, there is currently no adequate level of protection for data transfers to the United States. Data processing by U.S. services (such as Google Analytics) may result in data being processed and stored without being anonymized. Furthermore, U.S. government authorities may, in some cases, gain access to specific data. In addition, collected data may be linked to data from other services provided by the same provider, provided you have a corresponding user account. Whenever possible, we strive to use server locations within the EU, if such options are available.
We provide more detailed information about data transfers to third countries—where applicable—in the relevant sections of this Privacy Policy.
Data Processing Security
To protect personal data, we have implemented both technical and organizational measures. Whenever possible, we encrypt or pseudonymize personal data. By doing so, we make it as difficult as possible—within the limits of our capabilities—for third parties to infer personal information from our data.
Article 25 of the GDPR refers to “data protection through technology design and privacy-friendly default settings,” meaning that security must always be a priority—whether in software (e.g., forms) or hardware (e.g., access to the server room)—and appropriate measures must be implemented. Below, we will discuss specific measures as needed.
TLS Encryption with HTTPS
TLS, encryption, and HTTPS sound very technical—and they are. We use HTTPS (Hypertext Transfer Protocol Secure) to transmit data over the Internet in a way that prevents eavesdropping.
This means that the entire transmission of all data from your browser to our web server is secure—no one can “eavesdrop.”
This allows us to introduce an additional layer of security and comply with data protection through design (Article 25(1) of the GDPR). By using TLS (Transport Layer Security), an encryption protocol for secure data transmission over the Internet, we can ensure the protection of confidential data.
You can tell that this data transmission security measure is in use by the small padlock icon  in the upper-left corner of the browser, to the left of the web address (e.g., examplepage.de) and the use of the "https" scheme (instead of "http") as part of our web address.
If you'd like to learn more about encryption, we recommend searching Google for “Hypertext Transfer Protocol Secure wiki” to find useful links to additional information.
Communication
| Communication Summary 👥 Data Subjects: Anyone who communicates with us by phone, email, or online form 📓 Data Processed: e.g., phone number, name, email address, form data entered. You can find more details under the respective contact method 🤝 Purpose: Handling communication with customers, business partners, etc. 📅 Retention period: Duration of the business transaction and as required by law ⚖️ Legal basis: Art. 6(1)(a) GDPR (consent), Art. 6(1)(b) GDPR (contract), Art. 6(1)(f) GDPR (legitimate interests) |
If you contact us and communicate with us by phone, email, or through an online form, we may process your personal data.
The data is processed for the purpose of handling and addressing your inquiry and the related business transaction. The data is stored for as long as necessary or as required by law.
Affected Individuals
All individuals who contact us through the communication channels we provide are affected by the events mentioned above.
Phone
When you call us, the call data is stored in pseudonymized form on the respective device and with the telecommunications provider used. In addition, data such as your name and phone number may subsequently be sent via email and stored for the purpose of responding to your inquiry. The data is deleted as soon as the business transaction is complete and legal requirements permit.
When you communicate with us via email, data may be stored on the respective device (computer, laptop, smartphone, etc.) and on the email server. The data will be deleted as soon as the business matter has been resolved and legal requirements permit.
Online Forms
When you communicate with us via the online form, data is stored on our web server and, if necessary, forwarded to one of our email addresses. The data is deleted as soon as the business transaction is complete and legal requirements permit.
Legal Basis
The processing of data is based on the following legal grounds:
- Art. 6(1)(a) of the GDPR (Consent): You give us your consent to store your data and to use it for purposes related to the business transaction;
- Art. 6(1)(b) of the GDPR (Contract): It is necessary for the performance of a contract with you or a processor, such as a telephone service provider, or we must process the data for pre-contractual activities, such as preparing a quote;
- Art. 6(1)(f) GDPR (Legitimate Interests): We aim to handle customer inquiries and business communications in a professional manner. To do so, certain technical systems—such as email programs, Exchange servers, and mobile network providers—are necessary to ensure efficient communication.
Data Processing Agreement (DPA)
In this section, we’d like to explain what a data processing agreement is and why it’s necessary. Since the term “data processing agreement” is quite a tongue-twister, we’ll often use the acronym DPA throughout this text. Like most companies, we don’t operate alone; we also use services provided by other companies or individuals. By involving various companies or service providers, we may need to transfer personal data to them for processing. These partners then act as data processors, with whom we enter into a contract known as a Data Processing Agreement (DPA). The most important thing for you to know is that the processing of your personal data takes place exclusively in accordance with our instructions and must be governed by the DPA.
Who are data processors?
As a company and website owner, we are responsible for all data we process from you. In addition to the data controllers, there may also be so-called data processors. This includes any company or individual that processes personal data on our behalf. More specifically, and according to the GDPR definition: any natural or legal person, public authority, agency, or other body that processes personal data on our behalf is considered a data processor. Processors can therefore include service providers such as hosting or cloud providers, payment or newsletter providers, or large companies such as Google or Microsoft.
To help clarify the terminology, here is an overview of the three roles under the GDPR:
Data subject(you as a customer or prospective customer) → Data controller (we as a company and client) → Data processor (service providers such as web hosts or cloud providers)
Contents of a Data Processing Agreement
As mentioned above, we have entered into a Data Processing Agreement (DPA) with our partners who act as data processors. Above all, this agreement stipulates that the data processor shall process the data exclusively in accordance with the GDPR. The agreement must be concluded in writing; however, in this context, an electronic agreement is also considered “in writing.” The processing of personal data takes place only on the basis of this agreement. The agreement must include the following:
- Commitment to Us as the Data Controller
- Obligations and Rights of the Data Controller
- Categories of Data Subjects
- Type of Personal Data
- Nature and Purpose of Data Processing
- Purpose and Duration of Data Processing
- Location of Data Processing
Furthermore, the contract sets forth all of the data processor’s obligations. The most important obligations are:
- Measures to Ensure Data Security
- to take all necessary technical and organizational measures to protect the rights of the data subject
- to maintain a data processing register
- to cooperate with the data protection supervisory authority at its request
- to conduct a risk analysis with regard to the personal data received
- Sub-processors may only be engaged with the written authorization of the controller.
You can see what an AVV actually looks like, for example, at https://www.wko.at/service/wirtschaftsrecht-gewerberecht/eu-dsgvo-mustervertrag-auftragsverarbeitung.html. A sample contract is provided there.
Cookies
| Cookies Summary 👥 Data Subjects: Visitors to the website 🤝 Purpose: Depends on the specific cookie. For more details, see below or contact the software provider that sets the cookie. 📓 Data Processed: Depends on the specific cookie used. For more details, see below or contact the software provider that sets the cookie. 📅 Storage period: Depends on the specific cookie; may vary from hours to years ⚖️ Legal basis: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are cookies?
Our website uses HTTP cookies to store user-specific data.
Below, we explain what cookies are and why they are used, so that you can better understand the following privacy policy.
Whenever you browse the Internet, you use a browser. Some well-known browsers include Chrome, Safari, Firefox, Internet Explorer, and Microsoft Edge. Most websites store small text files in your browser. These files are called cookies.
One thing is undeniable: Cookies are really useful little helpers. Almost all websites use cookies. More specifically, they are HTTP cookies, since there are other types of cookies for different applications. HTTP cookies are small files that our website stores on your computer. These cookie files are automatically stored in the cookie folder—essentially the “brain” of your browser. A cookie consists of a name and a value. When defining a cookie, one or more attributes must also be specified.
Cookies store certain user data about you, such as your language or personal page settings. When you visit our site again, your browser sends this “user-specific” information back to our site. Thanks to cookies, our website knows who you are and provides you with the settings you’re used to. In some browsers, each cookie has its own file; in others, such as Firefox, all cookies are stored in a single file.
The following diagram illustrates a possible interaction between a web browser—such as Chrome—and a web server. In this scenario, the web browser requests a website and receives a cookie from the server, which the browser then uses again the next time a different page is requested.

There are both first-party cookies and third-party cookies. First-party cookies are created directly by our site, while third-party cookies are created by partner websites (e.g., Google Analytics). Each cookie must be evaluated individually, as each cookie stores different data. The expiration time of a cookie also varies from a few minutes to a few years. Cookies are not software programs and do not contain viruses, Trojans, or other “malware.” Cookies also cannot access information on your computer.
Here's an example of what cookie data might look like:
Name: _ga
Value:GA1.2.1326744211.152122077330-9
Purpose: To distinguish between website visitors
Expiration date:After 2 years
A browser should be able to support these minimum sizes:
- At least 4,096 bytes per cookie
- At least 50 cookies per domain
- At least 3,000 cookies in total
What types of cookies are there?
The specific cookies we use depend on the services we employ and are explained in the following sections of this Privacy Policy. At this point, we would like to briefly discuss the different types of HTTP cookies.
There are four types of cookies:
Essential Cookies
These cookiesare necessary to ensure the website’s basic functionality. For example, these cookies are needed when a user adds a product to the shopping cart, then continues browsing other pages, and only proceeds to checkout later. These cookies ensure that the shopping cart is not cleared, even if the user closes their browser window.
Functional Cookies
These cookies collect information about user behavior and whether the user receives any error messages. They are also used to measure the website's loading time and performance across different browsers.
Targeted Cookies
These cookies improve the user experience. For example, they store locations, font sizes, or form data that you have entered.
Advertising Cookies
These cookies are also called targeting cookies. They are used to deliver personalized ads to the user. This can be very convenient, but it can also be very annoying.
Usually, when you visit a website for the first time, you'll be asked which of these types of cookies you want to allow. And, of course, this decision is also stored in a cookie.
If you'd like to learn more about cookies and don't mind reading technical documentation, we recommend https://datatracker.ietf.org/doc/html/rfc6265, the Internet Engineering Task Force (IETF) Request for Comments titled “HTTP State Management Mechanism.”
Purpose of Processing via Cookies
The purpose ultimately depends on the specific cookie. You can find more details below or from the manufacturer of the software that sets the cookie.
What data is processed?
Cookies are small tools that help with a wide variety of tasks. Unfortunately, it is not possible to generalize about what data is stored in cookies, but we will inform you about the data that is processed or stored in this Privacy Policy.
Cookie Retention Periods
The storage period depends on the specific cookie and is explained in more detail below. Some cookies are deleted after less than an hour, while others may remain stored on a computer for several years.
You also have control over how long cookies are stored. You can manually delete all cookies at any time through your browser (see also “Right to Object” below). Furthermore, cookies that are based on your consent will be deleted no later than when you revoke your consent, although the lawfulness of their storage up to that point remains unaffected.
Right to Object – How Can I Delete Cookies?
You decide for yourself how and whether you want to use cookies. Regardless of which service or website the cookies come from, you always have the option to delete, disable, or allow only some cookies. For example, you can block third-party cookies but allow all other cookies.
If you want to see which cookies have been stored in your browser, or if you want to change or delete cookie settings, you can find these options in your browser settings:
Chrome: Delete, Enable, and Manage Cookies in Chrome
Safari: Managing Cookies and Website Data with Safari
Firefox: Clear cookies to remove data that websites have stored on your computer
Internet Explorer: Deleting and Managing Cookies
Microsoft Edge: Deleting and Managing Cookies
If you do not want to accept cookies at all, you can configure your browser to notify you whenever a cookie is about to be set. This allows you to decide for each individual cookie whether to allow it or not. The procedure varies depending on the browser. The best approach is to search for instructions on Google using the search terms “delete cookies Chrome” or “disable cookies Chrome” if you are using the Chrome browser.
Zur Verwaltung der eingesetzten Cookies und ähnlichen Technologien (Tracking-Pixel, Web-Beacons etc.) und diesbezüglicher Einwilligungen setzen wir das Consent Tool „Real Cookie Banner“ ein. Details zur Funktionsweise von „Real Cookie Banner“ findest du unter <a href=“https://devowl.io/de/rcb/datenverarbeitung/“ rel=“noreferrer“ target=“_blank“>https://devowl.io/de/rcb/datenverarbeitung/</a>.
Rechtsgrundlagen für die Verarbeitung von personenbezogenen Daten in diesem Zusammenhang sind Art. 6 Abs. 1 lit. c DS-GVO und Art. 6 Abs. 1 lit. f DS-GVO. Unser berechtigtes Interesse ist die Verwaltung der eingesetzten Cookies und ähnlichen Technologien und der diesbezüglichen Einwilligungen.
Die Bereitstellung der personenbezogenen Daten ist weder vertraglich vorgeschrieben noch für den Abschluss eines Vertrages notwendig. Du bist nicht verpflichtet die personenbezogenen Daten bereitzustellen. Wenn du die personenbezogenen Daten nicht bereitstellst, können wir deine Einwilligungen nicht verwalten.
Legal Basis
The so-called “Cookie Directives” have been in effect since 2009. They stipulate that the storage of cookies requires your consent (Article 6(1)(a) of the GDPR). However, reactions to these directives still vary widely among EU countries. In Austria, however, this directive was implemented in Section 96(3) of the Telecommunications Act (TKG). In Germany, the Cookie Directive was not transposed into national law. Instead, it was largely implemented in Section 15(3) of the Telemedia Act (TMG).
For strictly necessary cookies, even in the absence of consent, there are legitimate interests (Article 6(1)(f) of the GDPR), which are, in most cases, of an economic nature. We want to provide visitors to the website with a pleasant user experience, and certain cookies are often absolutely necessary to achieve this.
Unless strictly necessary cookies are used, this will only occur with your consent. The legal basis for this is Article 6(1)(a) of the GDPR.
The following sections provide more detailed information about the use of cookies, to the extent that the software used employs cookies.
Application Information
| Application Data Summary 👥 Data Subjects: Users who apply for a job with us 🤝 Purpose: Processing of the application procedure 📓 Data Processed: Name, address, contact information, email address, phone number, proof of qualifications (transcripts), and, if applicable, special categories of data. 📅 Retention period: If the application is successful, until the end of the employment relationship. Otherwise, the data will be deleted after the application process or stored for a certain period of time with your consent. ⚖️ Legal basis: Art. 6(1)(a) GDPR (consent), legitimate interest (Art. 6(1)(f) GDPR), Art. 6(1)(b) GDPR (contract), Art. 9(2)(a) GDPR (processing of special categories of data) |
What is application data?
You can apply for a position at our company by email, through our online form, or via a recruiting tool. All data we receive and process from you as part of an application is considered application data. In doing so, you will always disclose personal data such as your name, date of birth, address, and phone number.
Why do we process job application data?
We process your data so that we can conduct a proper selection process for the advertised position. In addition, we’d be happy to keep your application materials in our applicant database. This is because it often happens that, for a variety of reasons, a collaboration for the advertised position doesn’t work out, but we’re impressed by you and your application and can easily imagine working with you in the future. If you give us your consent, we’ll archive your materials so that we can easily contact you for future opportunities at our company.
We guarantee that we will handle your data with the utmost care and will always process it strictly within the legal framework. Even within our company, your data will only be shared with individuals who are directly involved in your application. In short: Your data is safe with us!
What data is processed?
For example, if you apply for a job with us via email, we will, of course, receive personal data as mentioned above. Even your email address is considered personal data. However, during the application process, we only process the data that is relevant to our decision on whether or not to welcome you to our team.
Exactly which data is processed depends primarily on the job posting. In most cases, however, it includes your name, date of birth, contact information, and proof of qualifications. If you submit your application via an online form, the data is transmitted to us in encrypted form. If you send us your application by email, this encryption does not take place. We therefore cannot assume any responsibility for the transmission process. However, once the data is on our servers, we are responsible for handling your data in accordance with the law.
During the application process, in addition to the information mentioned above, we may also request information about your health or ethnic origin so that both we and you can exercise our rights under labor law, social security, and social protection, while also fulfilling our corresponding obligations. This information constitutes special categories of data.
Here is a list of the types of data we may receive from you and process:
- Name
- Contact Information
- Email address
- Phone number
- Date of Birth
- Information contained in the cover letter and resume
- Proof of qualifications (e.g., diplomas)
- Special categories of data (e.g., ethnic origin, health information, religious beliefs)
- Usage data (websites visited, access data, etc.)
- Metadata (IP address, device information)
How long is the data stored?
When we hire you as a team member at our company, your data will be processed for the purposes of the employment relationship and retained by us at least until the employment relationship ends. All application documents will then be added to your employee file.
If we do not offer you the position, if you decline our offer, or if you withdraw your application, we may retain your data for up to 6 months after the conclusion of the application process based on our legitimate interest (Art. 6(1)(f) GDPR). After that, both your electronic data and all data from physical application documents will be completely deleted or destroyed. We retain your data, for example, so that we can still respond to any follow-up inquiries or, in the event of a legal dispute, provide evidence regarding the application. If a legal dispute arises and we may still need the data after the 6-month period has expired, we will not delete the data until there is no longer any reason to retain it. If there are statutory retention requirements to be met, we must generally store the data for longer than 6 months.
In addition, we may retain your data for a longer period if you have provided specific consent to do so. We do this, for example, if we can envision working with you in the future. In that case, it is helpful to have your data on file so that we can easily reach you. In this instance, your data will be added to our candidate pool. Of course, you can revoke your consent to the extended retention of your data at any time. If you do not revoke your consent and do not provide new consent, your data will be deleted after 2 years at the latest.
Legal Basis
The legal bases for the processing of your data are Article 6(1)(a) of the GDPR (consent), Article 6(1)(b) of the GDPR (contract or precontractual measures), Article 6(1)(f) of the GDPR (legitimate interests), and Article 9(2)(a) of the GDPR (processing of special categories of data).
If we add you to our applicant pool, we do so based on your consent (Art. 6(1)(a) GDPR). Please note that your consent to be included in our applicant pool is voluntary, has no impact on the application process, and you may withdraw your consent at any time. The lawfulness of the processing up until the time of withdrawal remains unaffected.
In cases involving the protection of vital interests, data processing is carried out in accordance with Article 9(2)(c) of the GDPR. For the purposes of healthcare, occupational medicine, medical diagnostics, care or treatment in the health or social sectors, or the administration of systems and services in the health or social sectors, the processing of personal data is carried out in accordance with Article 9(2)(h) of the GDPR. If you voluntarily provide special categories of personal data, the processing is based on Article 9(2)(a) of the GDPR.
Customer Data
| Customer Data Summary 👥 Data Subjects: Customers and business and contractual partners 🤝 Purpose: Provision of services agreed upon in a contract or pre-contractual agreement, including related communication 📓 Data Processed: Name, address, contact information, email address, phone number, payment information (such as invoices and bank details), contract details (such as the term and subject matter of the contract), IP address, order details 📅 Retention period: The data will be deleted as soon as it is no longer necessary for the fulfillment of our business purposes and there is no legal obligation to retain it. ⚖️ Legal basis: Legitimate interest (Art. 6(1)(f) GDPR), contract (Art. 6(1)(b) GDPR) |
What is customer data?
In order to provide our services and fulfill our contractual obligations, we also process data from our customers and business partners. This data always includes personal information. Customer data refers to all information processed on the basis of a contractual or pre-contractual relationship in order to provide the services we offer. Customer data, therefore, encompasses all the information we collect and process about our customers.
Why do we process customer data?
There are many reasons why we collect and process customer data. The most important one is that we simply need various types of data to provide our services. Sometimes your email address is all we need, but if you purchase a product or service, for example, we also need information such as your name, address, bank details, or contract information. We subsequently use this data for marketing and sales optimization so that we can improve our overall service for our customers. Another important aspect is our customer service, which is always very important to us. We want you to be able to contact us at any time with questions about our offerings, and for that, we need at least your email address.
What data is processed?
At this point, we can only describe the specific data we store in terms of categories. This is because it always depends on the services you receive from us. In some cases, you simply provide us with your email address so that we can, for example, contact you or answer your questions. In other cases, you purchase a product or service from us, and for that we need significantly more information, such as your contact information, payment details, and contract information.
Here is a list of the types of data we may receive from you and process:
- Name
- Contact Information
- Email address
- Phone number
- Date of Birth
- Payment information (invoices, bank information, payment history, etc.)
- Contract Details (Term, Content)
- Usage data (websites visited, access data, etc.)
- Metadata (IP address, device information)
How long is the data stored?
As soon as we no longer need the customer data to fulfill our contractual obligations and for our purposes, and the data is also not required for any potential warranty or liability obligations, we delete the relevant customer data. This is the case, for example, when a business contract ends. After that, the statute of limitations is generally 3 years, although longer periods are possible in individual cases. Of course, we also comply with statutory retention requirements. Your customer data will certainly not be disclosed to third parties unless you have explicitly given your consent.
Legal Basis
The legal bases for the processing of your data are Art. 6(1)(a) of the GDPR (consent), Article 6(1)(b) of the GDPR (contract or precontractual measures), Article 6(1)(f) of the GDPR (legitimate interests), and, in specific cases (e.g., medical services), Article 9(2)(a) of the GDPR (processing of special categories of data).
In cases involving the protection of vital interests, data processing is carried out in accordance with Article 9(2)(c) of the GDPR. For the purposes of healthcare, occupational medicine, medical diagnostics, care or treatment in the health or social sectors, or the administration of systems and services in the health or social sectors, the processing of personal data is carried out in accordance with Article 9(2)(h) of the GDPR. If you voluntarily provide special categories of personal data, the processing is based on Article 9(2)(a) of the GDPR.
Registration
| Registration Summary 👥 Data Subjects: All individuals who register, create an account, log in, and use the account. 📓 Data Processed: Email address, name, password, and other data collected during registration, login, and account use. 🤝 Purpose: To provide our services. To communicate with customers in connection with the services. 📅 Retention period:For as long as the company account associated with the texts exists, and generally for 3 years thereafter. ⚖️ Legal basis: Art. 6(1)(b) GDPR (contract), Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
When you register with us, we may process personal data if you enter personally identifiable information or if data such as your IP address is collected during the processing. You can read more below about what we mean by the rather cumbersome term “personal data.”
Please enter only the information we need for registration and for which you have a third party’s authorization, if you are registering on behalf of a third party. If possible, use a strong password that you do not use anywhere else and an email address that you check regularly.
Below, we provide you with information about the specific nature of our data processing, because we want you to feel comfortable with us!
What is registration?
When you register, we collect certain information from you, which allows you to easily log in online later and use your account with us. Having an account with us has the advantage that you don’t have to re-enter all your information every time. This saves time and effort and ultimately helps prevent errors in the delivery of our services.
Why do we process personal data?
In short, we process personal data to enable you to create and use an account with us.
If we didn’t do that, you’d have to enter all your information every time, wait for us to approve it, and then enter everything all over again. We—and many, many customers—wouldn’t like that very much. How would you feel about it?
What data is processed?
All data that you provided during registration, enter when logging in, or enter while managing your account information.
During registration, we process the following types of data:
- First Name
- Last Name
- Email address
- Company Name
- Street + House Number
- Place of Residence
- ZIP Code
- Country
When you sign up, we process the data you enter during registration—such as your username and password—as well as data collected in the background, such as device information and IP addresses.
When you use your account, we process data that you enter while using the account and that is generated in connection with your use of our services.
Retention period
We store the data you provide at least for as long as the account associated with that data remains active with us and is in use, for as long as contractual obligations between us exist, and, if the contract ends, until the respective claims arising from it become time-barred. In addition, we store your data for as long as and to the extent that we are subject to legal obligations to do so. Afterward, we retain transaction documents related to the contract (invoices, contract documents, account statements, etc.) as well as other relevant business records for the period required by law (typically several years).
Right to Object
Have you registered, entered your data, and now want to revoke your consent to its processing? No problem. As you can read above, under the General Data Protection Regulation, your rights remain in effect even during and after registration, sign-up, or the creation of an account with us. Please contact the Data Protection Officer listed above to exercise your rights. If you already have an account with us, you can easily view and manage your data and text within your account.
Legal Basis
By completing the registration process, you are entering into a pre-contractual relationship with us to conclude a user agreement for our platform (although this does not automatically result in a payment obligation). Youinvest time in entering data and registering, and we provide you with our services after you log in to our system and grant you access to your customer account. In addition, we fulfill our contractual obligations. Finally, we must keep registered users informed via email of any important changes. Thus, Article 6(1)(b) of the GDPR (implementation of pre-contractual measures, performance of a contract) applies.
In some cases, we may also seek your consent, for example, if you voluntarily provide more information than is strictly necessary or if you allow us to send you advertising. Article 6(1)(a) of the GDPR (Consent) therefore applies.
We also have a legitimate interest in knowing who we are dealing with in order to contact them in certain cases. In addition, we need to know who is using our services and whether they are being used in accordance with our Terms of Service; therefore, Article 6(1)(f) of the GDPR (Legitimate Interests) applies.
Note: Users should check the following sections (as needed):
Registration Using Your Real Name
Since we need to know who we are dealing with in the course of business, registration is only possible using your real name (real name) and not pseudonyms.
Registration Using Pseudonyms
You may use a pseudonym when registering, which means you do not have to register with us using your real name. This ensures that we cannot process your name.
Storage of the IP Address
During the registration, login, and account usage processes, we store the IP address in the background for security reasons so that we can verify legitimate use.
Public Profile
User profiles are publicly visible, meaning that parts of the profile can be viewed on the Internet even without entering a username and password.
Two-Factor Authentication (2FA)
Two-factor authentication (2FA) provides additional security during login, as it prevents you from logging in without a smartphone, for example. This technical measure to secure your account protects you from data loss or unauthorized access, even if your username and password were known. You can find out which 2FA method is used during registration, when logging in, and within your account itself.
Web Hosting Introduction
| Web Hosting Summary 👥 Data Subjects: Visitors to the website 🤝 Purpose: Professional hosting of the website and ensuring its operation 📓 Data Processed: IP address, time of website visit, browser used, and other data. More details can be found below or with the respective web hosting provider. 📅 Retention period: Depends on the respective provider, but generally 2 weeks ⚖️ Legal basis: Art. 6(1)(f) GDPR (Legitimate Interests) |
What is web hosting?
When you visit websites these days, certain information—including personal data—is automatically generated and stored, and this website is no exception. This data should be processed as sparingly as possible and only for a valid reason. By “website,” we mean the entirety of all web pages on a domain, i.e., everything from the home page to the very last subpage (like this one). By “domain,” we mean, for example, example.de or sampleexample.com.
If you want to view a website on a computer, tablet, or smartphone, you use a program called a web browser. You’re probably familiar with the names of some web browsers: Google Chrome, Microsoft Edge, Mozilla Firefox, and Apple Safari. We refer to them simply as browsers or web browsers.
To display a website, the browser must connect to another computer where the website's code is stored: the web server. Operating a web server is a complicated and time-consuming task, which is why it is usually handled by professional providers. These providers offer web hosting and ensure that website data is stored reliably and without errors. That’s a lot of technical terms, but please stick with it—it gets even better!
When the browser on your computer (desktop, laptop, tablet, or smartphone) establishes a connection and during the transmission of data to and from the web server, personal data may be processed. On the one hand, your computer stores data; on the other hand, the web server must also store data for a certain period of time to ensure proper operation.
A picture is worth a thousand words, so the following diagram illustrates the interaction between the browser, the Internet, and the hosting provider.

Why do we process personal data?
The purposes of data processing are:
- Professional website hosting and ensuring smooth operation
- to maintain operational and IT security
- Anonymous analysis of user behavior to improve our services and, if necessary, for law enforcement or to pursue legal claims
What data is processed?
Even as you are visiting our website right now, our web server—the computer on which this website is hosted—typically automatically stores data such as
- the complete web address (URL) of the webpage being viewed
- Browser and browser version (e.g., Chrome 87)
- the operating system used (e.g., Windows 10)
- the address (URL) of the previously visited page (referrer URL) (e.g., https://www.beispielquellsite.de/vondabinichgekommen/)
- the hostname and IP address of the device from which the request is being made (e.g., COMPUTERNAME and 194.23.43.121)
- Date and Time
- in files known as web server log files
How long is data stored?
As a general rule, the data listed above is stored for two weeks and then automatically deleted. We do not share this data with third parties; however, we cannot rule out the possibility that government authorities may access this data in the event of unlawful conduct.
In short: Your visit is logged by our provider (the company that hosts our website on special computers [servers]), but we will not share your information without your consent!
Legal Basis
The lawfulness of processing personal data in the context of web hosting is based on Article 6(1)(f) of the GDPR (protection of legitimate interests), as the use of professional hosting services from a provider is necessary to present the company on the Internet in a secure and user-friendly manner and, if necessary, to investigate any attacks or claims arising therefrom.
We generally have a contract with the hosting provider regarding data processing in accordance with Article 28 et seq. of the GDPR, which ensures compliance with data protection regulations and guarantees data security.
Hetzner Privacy Policy
We use Hetzner for our website; among other things, it is a web hosting provider. The service provider is the German company Hetzner Online GmbH, Industriestr. 25, 91710 Gunzenhausen, Germany.
For more information about the data processed when using Hetzner, please see the Privacy Policy at https://www.hetzner.com/de/legal/privacy-policy.
Hetzner Data Processing Agreement (DPA)
In accordance with Article 28 of the General Data Protection Regulation (GDPR), we have entered into a data processing agreement (DPA) with Hetzner. You can read more about what exactly a DPA is and, most importantly, what must be included in a DPA in our general section titled “Data Processing Agreement (DPA).”
This agreement is required by law because Hetzner processes personal data on our behalf. It specifies that Hetzner may only process data it receives from us in accordance with our instructions and must comply with the GDPR. You can find the link to the Data Processing Agreement (DPA) at https://docs.hetzner.com/de/general/general-terms-and-conditions/data-privacy-faq/.
Introduction to Web Analytics
| Web Analytics Privacy Policy Summary 👥 Data Subjects: Visitors to the website 🤝 Purpose: Analysis of visitor information to optimize the website. 📓 Data Processed: Access statistics, which include data such as visitor locations, device information, duration and time of access, navigation behavior, click behavior, and IP addresses. You can find more details on this in the documentation for the respective web analytics tool. 📅 Retention period: Depends on the web analytics tool used ⚖️ Legal basis: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Web Analytics?
We use software on our website to analyze the behavior of website visitors, commonly referred to as web analytics. This process involves the collection of data, which the respective analytics tool provider (also known as a tracking tool) stores, manages, and processes. This data is used to generate analyses of user behavior on our website, which are then made available to us as the website operator. In addition, most tools offer various testing options. For example, this allows us to test which offers or content are most popular with our visitors. To do this, we show you two different offers for a limited period of time. After the test (known as an A/B test), we know which product or content our website visitors find more interesting. For such testing procedures, as well as for other analytics procedures, user profiles may be created and the data stored in cookies.
Why do we use web analytics?
With our website, we have a clear goal in mind: we want to provide the best online experience in our industry. To achieve this goal, we aim to offer the best and most engaging content while also ensuring that you feel completely at home on our website. Using web analytics tools, we can take a closer look at how our website visitors behave and then improve our website for both you and us accordingly. For example, we can determine the average age of our visitors, where they come from, when our website receives the most traffic, and which content or products are particularly popular. All of this information helps us optimize the website and tailor it to best meet your needs, interests, and preferences.
What data is processed?
Exactly which data is stored depends, of course, on the analytics tools used. However, as a general rule, the data stored includes, for example, the content you view on our website, the buttons or links you click, when you visit a page, the browser you use, the device (PC, tablet, smartphone, etc.) you use to visit the website, and the operating system you use. If you have consented to the collection of location data, this information may also be processed by the web analytics provider.
In addition, your IP address is also stored. According to the General Data Protection Regulation (GDPR), IP addresses are considered personal data. However, your IP address is generally stored in a pseudonymized form (i.e., in an unrecognizable and truncated form). For the purposes of testing, web analytics, and web optimization, no direct data—such as your name, age, address, or email address—is stored. All such data, if collected, is stored in a pseudonymized form. This means you cannot be identified as an individual.
The following example schematically illustrates how Google Analytics works as an example of client-side web tracking using JavaScript code.

How long the respective data is stored always depends on the provider. Some cookies store data for only a few minutes or until you leave the website; others can store data for several years.
Duration of Data Processing
We provide information below regarding the duration of data processing, to the extent that we have further details on this matter. In general, we process personal data only for as long as is strictly necessary to provide our services and products. If required by law—as is the case with accounting, for example—this retention period may be exceeded.
Right to Object
You also have the right and the option to revoke your consent to the use of cookies or third-party providers at any time. You can do this either through our cookie management tool or through other opt-out features. For example, you can also prevent data collection via cookies by managing, disabling, or deleting cookies in your browser.
Legal Basis
The use of web analytics requires your consent, which we have obtained through our cookie pop-up. Pursuant to Article 6(1)(a) of the GDPR (Consent), this consent constitutes the legal basis for the processing of personal data, such as may occur when data is collected by web analytics tools.
In addition to consent, we have a legitimate interest in analyzing the behavior of website visitors in order to improve our offerings both technically and economically. With the help of web analytics, we detect website errors, identify attacks, and improve cost-effectiveness. The legal basis for this is Article 6(1)(f) of the GDPR (Legitimate Interests). However, we only use these tools if you have given your consent.
Since web analytics tools use cookies, we also recommend that you read our general privacy policy regarding cookies. To find out exactly what data about you is stored and processed, you should review the privacy policies of the respective tools.
Information on specific web analytics tools—if available—can be found in the following sections.
Facebook Pixel Privacy Policy
We use Facebook's Facebook Pixel on our website. To do this, we have implemented a code snippet on our website. The Facebook Pixel is a snippet of JavaScript code that loads a set of functions that allow Facebook to track your user actions if you arrived at our website via Facebook Ads. For example, if you purchase a product on our website, the Facebook Pixel is triggered and stores your actions on our website in one or more cookies. These cookies enable Facebook to match your user data (customer data such as IP address and user ID) with the data from your Facebook account. Facebook then deletes this data. The data collected is anonymous to us and cannot be viewed by us; it is used solely for the purpose of serving advertisements. If you are a Facebook user and are logged in, your visit to our website is automatically associated with your Facebook user account.
We want to show our services and products only to those people who are genuinely interested in them. With the help of Facebook Pixel, our advertising campaigns can be better tailored to your preferences and interests. This way, Facebook users (provided they have enabled personalized ads) see ads that are relevant to them. Facebook also uses the collected data for analytical purposes and to create its own ads.
Below, we list the cookies that were set by embedding Facebook pixels on a test page. Please note that these are only example cookies. Different cookies are set depending on your interactions on our website.
Name: _fbp
Value: fb.1.1568287647279.257405483-6122077330-7
Purpose: Facebook uses this cookie to display advertising.
Expiration date: after 3 months
Name:fr
Value: 0aPf312HOS5Pboo2r..Bdeiuf…1.0.Bdeiuf.
Purpose: This cookie is used to ensure that Facebook Pixel functions properly.
Expiration date: after 3 months
Name: comment_author_50ae8267e2bdf1253ec1a5769f48e062122077330-3
Value: Author's name
Purpose: This cookie stores the text and name of a user who, for example, leaves a comment.
Expiration date: after 12 months
Name: comment_author_url_50ae8267e2bdf1253ec1a5769f48e062
Value: https%3A%2F%2Fwww.testseite…%2F (author's URL)
Purpose: This cookie stores the URL of the website that the user enters in a text field on our website.
Expiration date: after 12 months
Name: comment_author_email_50ae8267e2bdf1253ec1a5769f48e062
Value: Author's email address
Purpose: This cookie stores the user's email address if the user has provided it on the website.
Expiration date: after 12 months
Note: Thecookies listed above are based on individual user behavior. When it comes to the use of cookies in particular, changes on Facebook can never be ruled out.
If you are logged into Facebook, you can change your ad settings yourself at https://www.facebook.com/adpreferences/advertisers/. If you are not a Facebook user, you can generally manage your usage-based online advertising at https://www.youronlinechoices.com/de/praferenzmanagement/. There, you have the option to disable or enable providers.
Facebook processes your data in the United States, among other places. Facebook, or Meta Platforms, is an active participant in the EU-U.S. Data Privacy Framework, which governs the proper and secure transfer of personal data from EU citizens to the U.S. For more information, please visit https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Facebook uses so-called Standard Contractual Clauses (Art. 46, paras. 2 and 3 of the GDPR). Standard Contractual Clauses (SCCs) are model clauses provided by the European Commission and are intended to ensure that your data complies with European data protection standards even when it is transferred to and stored in third countries (such as the United States). Through the EU-U.S. Data Privacy Framework and the Standard Contractual Clauses, Facebook commits to adhering to European data protection standards when processing your relevant data, even if the data is stored, processed, and managed in the U.S. These clauses are based on an implementing decision by the European Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
Facebook's Data Processing Terms, which refer to the Standard Contractual Clauses, can be found at https://www.facebook.com/legal/terms/dataprocessing.
If you would like to learn more about Facebook's privacy practices, we recommend reviewing the company's privacy policy at https://www.facebook.com/privacy/policy.
Matomo Privacy Policy
We use Matomo, a website analytics tool, on our website. The service provider is the New Zealand-based company InnoCraft Ltd, 7 Waterloo Quay PO625, 6140 Wellington, New Zealand.
For more information about the data processed through the use of Matomo, please see the Privacy Policy at https://matomo.org/privacy-policy/. You can direct any questions regarding data protection by email to privacy@matomo.org.
Matomo On-Premise Privacy Policy
We use the privacy-friendly analytics program Matomo On-Premise on our website. With the on-premise version, Matomo is installed on our own server. This means we act as the operator of the software, and any data we may collect from you is stored directly with us. Data processing therefore remains entirely under our control. The service provider is the New Zealand-based company InnoCraft Ltd, 7 Waterloo Quay PO625, 6140 Wellington, New Zealand.
If you would like to learn more about data processing by Matomo On-Premise, please feel free to contact us. We also recommend reviewing Matomo’s privacy policy at https://matomo.org/privacy-policy/.
Matomo On-Premise (without cookies)
Many web analytics tools commonly use so-called cookies to collect and process a significant amount of personal data for analytical purposes and for their own marketing. Cookies are small text files that are typically stored in your browser and may contain personal data. We want to respect and protect your privacy as much as possible. That is why we have decided to take a different approach and use Matomo On-Premise entirely without cookies. Although we can perform various measurements and web analytics with Matomo, no personal data about you is stored in cookies during this process. Matomo On-Premise without cookies is one of the most privacy-friendly web analytics services on the market.
Email Marketing Introduction
| Email Marketing Summary 👥 Data Subjects: Newsletter subscribers 🤝 Purpose: Direct marketing via email, notifications about system-related events 📓 Data Processed: Data entered during registration, but at a minimum the email address. You can find more details about this in the respective email marketing tool used. 📅 Retention period: For the duration of the subscription ⚖️ Legal basis: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is email marketing?
To keep you up to date, we also use email marketing. In this context, provided you have consented to receiving our emails or newsletters, your data will also be processed and stored. Email marketing is a subset of online marketing. It involves sending news or general information about a company, its products, or its services via email to a specific group of people who are interested in such content.
If you would like to subscribe to our email marketing (usually via newsletter), you normally just need to sign up with your email address. To do so, simply fill out an online form and submit it. However, we may also ask you for your title and first and last name so that we can address you personally.
In general, newsletter sign-ups work using the so-called “double opt-in process.” After you sign up for our newsletter on our website, you will receive an email asking you to confirm your subscription. This ensures that the email address belongs to you and that no one has signed up using someone else’s email address. We, or a notification tool we use, log every single subscription. This is necessary so that we can verify that the subscription process was carried out in accordance with the law. Typically, the time of subscription, the time of subscription confirmation, and your IP address are stored. Additionally, any changes you make to your stored data are also logged.
Why do we use email marketing?
Of course, we want to stay in touch with you and keep you updated on the most important news about our company. To that end, we use email marketing—often simply referred to as a “newsletter”—as a key component of our online marketing strategy. Provided you give your consent or it is permitted by law, we will send you newsletters, system emails, or other notifications via email. When we use the term “newsletter” in the following text, we are referring primarily to emails sent on a regular basis. Of course, we do not want to bother you in any way with our newsletters. That is why we always strive to provide only relevant and interesting content. For example, you’ll learn more about our company, our services, or our products. Since we’re constantly improving our offerings, you’ll also be informed via our newsletter whenever there’s news or when we’re currently offering special, lucrative promotions. If we engage a service provider that offers a professional email distribution tool for our email marketing, we do so to ensure we can deliver newsletters to you quickly and securely. The primary purpose of our email marketing is to inform you about new offers and to help us achieve our business goals.
What data is processed?
If you subscribe to our newsletter through our website, you confirm your membership in an email list via email. In addition to your IP address and email address, your title, name, address, and phone number may also be stored—but only if you consent to this data storage. The data marked as such is necessary for you to use the service we offer. Providing this information is voluntary; however, failure to do so will prevent you from using the service. In addition, information about your device or your preferred content on our website may also be stored. For more information on data storage when you visit a website, see the section “Automatic Data Storage.” We record your declaration of consent so that we can always demonstrate that it complies with our laws.
Duration of Data Processing
If you unsubscribe from our email/newsletter mailing list, we may retain your email address for up to three years based on our legitimate interests, so that we can still provide evidence of your consent at that time. We may process this data only if we need to defend ourselves against any potential claims.
However, if you confirm that you have given us your consent to subscribe to the newsletter, you may submit an individual request to have your information deleted at any time. If you permanently revoke your consent, we reserve the right to add your email address to a block list. As long as you have voluntarily subscribed to our newsletter, we will, of course, continue to retain your email address.
Right to Object
You can unsubscribe from our newsletter at any time. To do so, simply revoke your consent to receive the newsletter. This usually takes just a few seconds or one or two clicks. You’ll usually find a link to unsubscribe from the newsletter right at the bottom of each email. If you really can’t find the link in the newsletter, please contact us by email and we’ll cancel your newsletter subscription immediately.
Legal Basis
We send our newsletter based on your consent (Article 6(1)(a) of the GDPR). This means that we may only send you a newsletter if you have actively subscribed to it beforehand. We may also send you promotional messages if you have become our customer and have not objected to the use of your email address for direct marketing.
Information about specific email marketing services and how they process personal data—if available—can be found in the following sections.
Click-Tip Privacy Policy
We use Klick-Tipp, a marketing automation service, on our website. The service provider is the British company Klick-Tipp Limited, 15 Cambridge Court, 210 Shepherd’s Bush Road, London W67NJ, United Kingdom. You can learn more about the data processed through the use of Klick-Tipp in the Privacy Policy at https://www.klicktipp.com/datenschutzerklarung/.
Social Media Introduction
| Social Media Privacy Policy Summary 👥 Data Subjects: Visitors to the website 🤝 Purpose: To present and optimize our services, to contact visitors, prospective customers, and others, and for advertising 📓 Data Processed: Data such as phone numbers, email addresses, contact information, user behavior data, information about your device, and your IP address. You can find more details on the respective social media tool used. 📅 Retention period: Depends on the social media platforms used ⚖️ Legal basis: Art. 6(1)(a) GDPR (Consent), Art. 6(1)(f) GDPR (Legitimate Interests) |
What is social media?
In addition to our website, we are also active on various social media platforms. In this context, user data may be processed so that we can specifically target users who are interested in us through social networks. Furthermore, elements of a social media platform may be embedded directly into our website. This is the case, for example, when you click on a “social button” on our website and are redirected directly to our social media presence. The term “social media” refers to websites and apps through which registered members can create content, share content publicly or within specific groups, and connect with other members.
Why do we use social media?
For years, social media platforms have been the place where people communicate and connect online. Through our social media presence, we can introduce our products and services to potential customers. The social media elements embedded on our website help you quickly and easily access our social media content.
The data stored and processed through your use of a social media channel is primarily intended to enable web analytics. The goal of these analytics is to develop more precise and personalized marketing and advertising strategies. Depending on your behavior on a social media platform, the analyzed data can be used to draw relevant conclusions about your interests and create so-called user profiles. This also enables the platforms to present you with tailored advertisements. In most cases, cookies are placed in your browser for this purpose to store data about your usage behavior.
We generally assume that we remain the data controller under data protection law, even when we use the services of a social media platform. However, the European Court of Justice has ruled that, in certain cases, the operator of the social media platform may be jointly responsible with us within the meaning of Article 26 of the GDPR. Where this is the case, we will specifically note this and operate on the basis of a relevant agreement. The key provisions of the agreement are then set forth below for the respective platform.
Please note that when you use social media platforms or our embedded features, your data may also be processed outside the European Union, as many social media channels—such as Facebook or Twitter—are U.S. companies. As a result, you may no longer be able to assert or enforce your rights regarding your personal data as easily.
What data is processed?
Exactly which data is stored and processed depends on the specific social media platform provider. However, it usually includes data such as phone numbers, email addresses, information you enter into a contact form, user data—for example, which buttons you click, who you like or follow, and when you visited which pages—as well as information about your device and your IP address. Most of this data is stored in cookies. Especially if you have a profile on the social media platform you’re visiting and are logged in, data can be linked to your profile.
All data collected through a social media platform is also stored on the providers' servers. Consequently, only the providers have access to the data and can provide you with the relevant information or make changes.
If you want to know exactly what data is stored and processed by social media providers and how you can object to the processing of your data, you should carefully read the company’s privacy policy. If you have questions about data storage and processing or wish to exercise your rights in this regard, we recommend that you contact the provider directly.
Duration of Data Processing
We provide information below regarding the duration of data processing, to the extent that we have further details. For example, the social media platform Facebook stores data until it is no longer needed for its own purposes. However, customer data that is matched with your own user data is deleted within two days. In general, we process personal data only for as long as is strictly necessary to provide our services and products. If required by law—as is the case with accounting, for example—this retention period may be exceeded.
Right to Object
You also have the right and the option at any time to withdraw your consent to the use of cookies or third-party providers, such as embedded social media elements. You can do this either through our cookie management tool or through other opt-out features. For example, you can also prevent data collection via cookies by managing, disabling, or deleting cookies in your browser.
Since social media tools may use cookies, we also recommend that you review our general privacy policy regarding cookies. To find out exactly what data about you is stored and processed, you should read the privacy policies of the respective tools.
Legal Basis
If you have consented to the processing and storage of your data through embedded social media elements, this consent serves as the legal basis for data processing (Art. 6(1)(a) GDPR). In general, if consent has been given, your data is also stored and processed based on our legitimate interest (Art. 6(1)(f) GDPR) in maintaining prompt and effective communication with you or other customers and business partners. However, we only use these tools to the extent that you have provided your consent. Most social media platforms also set cookies in your browser to store data. We therefore recommend that you carefully read our privacy policy regarding cookies and review the privacy policy or cookie guidelines of the respective service provider.
You can find information about specific social media platforms—if available—in the following sections.
LinkedIn Privacy Policy
| LinkedIn Privacy Policy Summary 👥 Data Subjects: Visitors to the website 🤝 Purpose: Optimization of our services 📓 Data Processed: Data such as user behavior data, information about your device, and your IP address. You can find more details below in the privacy policy. 📅 Retention period: The data is generally deleted within 30 days ⚖️ Legal basis: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is LinkedIn?
We use social plugins from the social media network LinkedIn, operated by LinkedIn Corporation, 2029 Stierlin Court, Mountain View, CA 94043, USA, on our website. These social plugins may include feeds, content sharing, or links to our LinkedIn page. The social plugins are clearly marked with the familiar LinkedIn logo and allow users, for example, to share interesting content directly from our website. For the European Economic Area and Switzerland, LinkedIn Ireland Unlimited Company, located at Wilton Place in Dublin, is responsible for data processing.
When such plug-ins are embedded, data may be sent to LinkedIn, stored there, and processed. In this privacy policy, we aim to inform you about what data is involved, how the network uses this data, and how you can manage or prevent the storage of this data.
LinkedIn is the largest social network for professional connections. Unlike Facebook, for example, the company focuses exclusively on building professional connections. Companies can use the platform to showcase their services and products and establish business relationships. Many people also use LinkedIn to look for jobs or to find suitable employees for their own companies. In Germany alone, the network has over 11 million members. In Austria, there are about 1.3 million.
Why do we use LinkedIn on our website?
We know how busy you are. It’s not possible to keep track of all social media channels individually. Even if, as in our case, it would be worth the effort. That’s because we regularly post interesting news or articles that are worth sharing. That’s why we’ve added a feature to our website that lets you share interesting content directly on LinkedIn or link directly to our LinkedIn page. We view embedded social plugins as an added service on our website. The data that LinkedIn collects also helps us ensure that any advertising we run is shown only to people who are interested in what we have to offer.
What data does LinkedIn store?
LinkedIn does not store any personal data simply by embedding social plug-ins. LinkedIn refers to this data, which is generated by plug-ins, as “passive impressions.” However, if you click on a social plug-in—for example, to share our content—the platform stores personal data as so-called “active impressions.” This happens regardless of whether you have a LinkedIn account or not. If you are logged in, the collected data is associated with your account.
Your browser establishes a direct connection to LinkedIn’s servers when you interact with our plug-ins. This allows the company to log various usage data. In addition to your IP address, this may include, for example, login data, device information, or details about your Internet or mobile service provider. If you access LinkedIn services via your smartphone, your location may also be determined (after you have given your consent). LinkedIn may also share this data in “hashed” form with third-party advertisers. Hashing means that a data record is converted into a string of characters. This allows the data to be encrypted in such a way that individuals can no longer be identified.
Most of the data regarding your user behavior is stored in cookies. These are small text files that are usually placed in your browser. In addition, LinkedIn may also use web beacons, pixel tags, ad tags, and other device identifiers.
Various tests also show which cookies are set when a user interacts with a social plugin. The data found is not intended to be exhaustive and is provided solely as an example. The following cookies were set without being logged in to LinkedIn:
Name: bcookie
Value: =2&34aab2aa-2ae1-4d2a-8baf-c2e2d7235c16122077330-
Purpose: This cookie is a so-called "browser ID cookie" and therefore stores your identification number (ID).
Expiration date: After 2 years
Name: lang
Value: v=2&lang=de-de
Purpose: This cookie stores your default or preferred language.
Expiration date: at the end of the session
Name: lidc
Value: 1818367:t=1571904767:s=AQF6KNnJ0G122077330…
Purpose: This cookie is used for routing. Routing tracks the paths you took to get to LinkedIn and how you navigate through the website.
Expiration date: after 24 hours
Name: rtc
Value: kt0lrv3NF3x3t6xvDgGrZGDKkX
Purpose:No further information could be found about this cookie.
Expiration date: after 2 minutes
Name: JSESSIONID
Value: ajax:1220773302900777718326218137
Purpose: This is a session cookie that LinkedIn uses to maintain anonymous user sessions on the server.
Expiration Date: at the end of the session
Name: bscookie
Value: “v=1&201910230812…
Purpose: This cookie is a security cookie. LinkedIn describes it as a Secure Browser ID cookie.
Expiration date: after 2 years
Name: fid
Value: AQHj7Ii23ZBcqAAAA…
Purpose: No further information could be found about this cookie.
Expiration date: after 7 days
Note: LinkedIn also works with third-party providers. That is why we detected the two Google Analytics cookies, _ga and _gat, during our test.
How long and where is the data stored?
In general, LinkedIn retains your personal data for as long as the company deems necessary to provide its services. However, LinkedIn deletes your personal data when you delete your account. In some exceptional cases, LinkedIn retains certain data in aggregated and anonymized form even after you delete your account. Once you delete your account, other people will no longer be able to view your data within one day. LinkedIn generally deletes the data within 30 days. However, LinkedIn retains data if required to do so by law. Data that can no longer be linked to specific individuals remains stored even after the account is closed. The data is stored on various servers in the United States and presumably also in Europe.
How can I delete my data or prevent it from being stored?
You have the right to access and delete your personal data at any time. You can manage, edit, and delete your data in your LinkedIn account. You can also request a copy of your personal data from LinkedIn.
Here's how to access the account information on your LinkedIn profile:
On LinkedIn, click your profile icon and select "Settings & Privacy." Next, click "Privacy," and then click "Change" in the "How LinkedIn uses your data" section. In just a few moments, you'll be able to download selected data about your web activity and account history.
You also have the option to prevent LinkedIn from processing your data directly in your browser. As mentioned above, LinkedIn stores most of its data using cookies that are placed in your browser. You can manage, disable, or delete these cookies. The process varies slightly depending on which browser you use. Under the “Cookies” section, you’ll find links to the relevant instructions for the most popular browsers.
You can also configure your browser so that you are always notified when a cookie is about to be set. This allows you to decide on a case-by-case basis whether you want to accept the cookie or not.
Legal Basis
If you have consented to the processing and storage of your data through embedded social media elements, this consent serves as the legal basis for data processing (Art. 6(1)(a) GDPR). In general, your data is also stored and processed based on our legitimate interest (Art. 6(1)(f) GDPR) in maintaining prompt and effective communication with you or other customers and business partners. However, we only use the embedded social media elements to the extent that you have given your consent. Most social media platforms also set cookies in your browser to store data. Therefore, we recommend that you carefully read our privacy policy regarding cookies and review the privacy policy or cookie guidelines of the respective service provider.
LinkedIn processes your data in the United States, among other places. Please note that, in the opinion of the European Court of Justice, there is currently no adequate level of protection for data transfers to the United States. This may entail various risks regarding the lawfulness and security of data processing.
LinkedIn uses so-called Standard Contractual Clauses (Art. 46, paras. 2 and 3 of the GDPR) as the basis for data processing by recipients based in third countries (outside the European Union, Iceland, Liechtenstein, and Norway—specifically, the United States) or for data transfers to such countries. Standard Contractual Clauses (SCCs) are model templates provided by the European Commission and are intended to ensure that your data complies with European data protection standards even when it is transferred to and stored in third countries (such as the United States). Through these clauses, LinkedIn commits to adhering to European data protection standards when processing your relevant data, even if the data is stored, processed, and managed in the U.S. These clauses are based on an implementing decision by the European Commission. You can find the decision and the corresponding Standard Contractual Clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
For more information about the standard contractual clauses on LinkedIn, visit https://de.linkedin.com/legal/l/dpa or https://www.linkedin.com/legal/l/eu-sccs.
We have tried to provide you with the most important information about how LinkedIn processes data. Visit https://www.linkedin.com/legal/privacy-policy to learn more about how the social media network LinkedIn processes data.
Data Processing Agreement (DPA) LinkedIn
In accordance with Article 28 of the General Data Protection Regulation (GDPR), we have entered into a data processing agreement (DPA) with LinkedIn. You can read more about what exactly a DPA is and, most importantly, what must be included in a DPA in our general section titled “Data Processing Agreement (DPA).”
This agreement is required by law because LinkedIn processes personal data on our behalf. It specifies that LinkedIn may only process data it receives from us in accordance with our instructions and must comply with the GDPR. You can find the link to the Data Processing Agreement (DPA) at https://de.linkedin.com/legal/l/dpa.
Pinterest Privacy Policy
| Pinterest Privacy Policy Summary 👥 Data Subjects: Visitors to the website 🤝 Purpose: To optimize our services 📓 Data Processed: Data such as user behavior data, information about your device, your IP address, and search terms. You can find more details below in the privacy policy. 📅 Retention period: until Pinterest no longer needs the data for its purposes ⚖️ Legal basis: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Pinterest?
On our website, we use buttons and widgets from the social media network Pinterest, operated by Pinterest Inc., 808 Brannan Street, San Francisco, CA 94103, USA. For the European region, the Irish company Pinterest Europe Ltd. (Palmerston House, 2nd Floor, Fenian Street, Dublin 2, Ireland) is responsible for all data protection-related matters.
Pinterest is a social network that specializes in visual content and photographs. The name is a combination of the words “pin” and “interest.” Users can share their hobbies and interests on Pinterest and view each other’s profiles—featuring images—either publicly or within specific groups.
Why do we use Pinterest?
Pinterest has been around for several years now, and this social media platform remains one of the most visited and valued platforms. Pinterest is particularly well-suited for our industry because the platform is primarily known for its beautiful and interesting images. That’s why we’re naturally active on Pinterest and want to showcase our content there as well, beyond our website. The data collected may also be used for advertising purposes so that we can show promotional messages to exactly those people who are interested in our services or products.
What data does Pinterest process?
So-called log data may be stored. This includes information about your browser, IP address, the address of our website, and the activities you perform on it (for example, when you click the "Save" or "Pin" button), search histories, the date and time of the request, and cookie and device data. When you interact with an embedded Pinterest feature, cookies that store various types of data may also be set in your browser. In most cases, the log data mentioned above, default language settings, and clickstream data are stored in cookies. Pinterest defines clickstream data as information about your website behavior.
If you have a Pinterest account and are logged in, the data collected through our site may be added to your account and used for advertising purposes. When you interact with our embedded Pinterest features, you are typically redirected to the Pinterest site. Here is a sample list of cookies that are then set in your browser.
Name: _auth
Value: 0
Purpose: This cookie is used for authentication. It can store, for example, a value such as your “username.”
Expiration date: after one year
Name: _pinterest_referrer
Value: 1
Purpose: This cookie records that you arrived at Pinterest via our website. It therefore stores the URL of our website:
Expiration date: at the end of the session
Name: _pinterest_sess
Value: …9HRHZvVE0rQlUxdG89
Purpose: This cookie is used for logging in to Pinterest and contains user IDs, authentication tokens, and timestamps.
Expiration date: after one year
Name: _routing_id
Value: “8d850ddd-4fb8-499c-961c-77efae9d4065122077330-8”
Purpose: This cookie contains an assigned value that is used to identify a specific routing destination.
Expiration date: after one day
Name: cm_sub
Value: denied
Purpose: This cookie stores a user ID and a timestamp.
Expiration date: after one year
Name: csrftoken
Value: 9e49145c82a93d34fd933b0fd8446165122077330-1
Purpose: This cookie is most likely set for security reasons to prevent forged requests. However, we were unable to determine the exact purpose.
Expiration date: after one year
Name: sessionFunnelEventLogged
Value: 1
Purpose: We have not yet been able to obtain any further informationabout this cookie.
Expiration date: after one day
How long and where is the data stored?
Pinterest generally stores the collected data until it is no longer needed for the company’s purposes. As soon as data retention is no longer necessary—for example, to comply with legal requirements—the data is either deleted or anonymized so that you can no longer be identified as an individual. The data may also be stored on servers in the United States.
Right to Object
You also have the right and the option to revoke your consent to the use of cookies or third-party providers such as Pinterest at any time. You can do this either through our cookie management tool or through other opt-out features. For example, you can also prevent data collection via cookies by managing, disabling, or deleting cookies in your browser.
Since embedded Pinterest elements may use cookies, we also recommend that you review our general privacy policy regarding cookies. To find out exactly what data about you is stored and processed, you should read the privacy policies of the respective tools.
Legal Basis
If you have consented to the processing and storage of your data through embedded social media elements, this consent serves as the legal basis for the data processing (Art. 6(1)(a) GDPR). In general, your data is also stored and processed based on our legitimate interest (Art. 6(1)(f) GDPR) in maintaining prompt and effective communication with you or other customers and business partners. However, we only use this tool if you have given your consent. Most social media platforms also set cookies in your browser to store data. Therefore, we recommend that you carefully read our privacy policy regarding cookies and review the privacy policy or cookie policy of the respective service provider.
Pinterest processes your data in the United States, among other places. Please note that, in the opinion of the European Court of Justice, there is currently no adequate level of protection for data transfers to the United States. This may entail various risks regarding the lawfulness and security of data processing.
Pinterest uses so-called Standard Contractual Clauses (Art. 46, paras. 2 and 3 of the GDPR) as the basis for data processing by recipients located in third countries (outside the European Union, Iceland, Liechtenstein, and Norway—specifically, the United States) or for data transfers to those countries. Standard Contractual Clauses (SCCs) are model clauses provided by the European Commission and are intended to ensure that your data complies with European data protection standards even when it is transferred to and stored in third countries (such as the United States). Through these clauses, Pinterest commits to adhering to European data protection standards when processing your relevant data, even if the data is stored, processed, and managed in the United States. These clauses are based on an implementing decision by the European Commission. You can find the decision and the corresponding Standard Contractual Clauses here: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de.
For more information about Pinterest's Standard Contractual Clauses, visit https://policy.pinterest.com/de/privacy-policy#section-residents-of-the-eea.
We have tried to provide you with the most important information about how Pinterest processes data. You can learn more about Pinterest's privacy policy at https://policy.pinterest.com/de/privacy-policy.
Twitter Privacy Policy
| Twitter Privacy Policy Summary 👥 Data Subjects: Visitors to the website 🤝 Purpose: To optimize our services 📓 Data Processed: Data such as user behavior data, information about your device, and your IP address. You can find more details on this further down in the privacy policy. 📅 Retention period: Twitter deletes data collected from other websites after 30 days at the latest ⚖️ Legal basis: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Twitter?
We have integrated Twitter features into our website. These include, for example, embedded tweets, timelines, buttons, and hashtags. Twitter is a microblogging service and social media platform operated by Twitter Inc., One Cumberland Place, Fenian Street, Dublin 2 D02 AX07, Ireland.
To the best of our knowledge, simply embedding Twitter features in the European Economic Area and Switzerland does not result in the transfer of any personal data or data regarding your web activities to Twitter. Only when you interact with Twitter features—such as clicking a button—can data be sent to Twitter, where it is stored and processed. We have no control over this data processing and bear no responsibility for it. In this Privacy Policy, we aim to provide you with an overview of what data Twitter stores, what Twitter does with this data, and how you can largely protect yourself against data transfer.
For some, Twitter is a news service; for others, a social media platform; and still others refer to it as a microblogging service. All of these terms are valid and mean more or less the same thing.
Both individuals and businesses use Twitter to communicate with interested people via short messages. Twitter allows only 280 characters per message. These messages are called “tweets.” Unlike Facebook, for example, the service does not focus on building a network of “friends,” but rather aims to be seen as a global and open messaging platform. On Twitter, users can also maintain an anonymous account, and tweets can be deleted either by the company or by the users themselves.
Why do we use Twitter on our website?
Like many other websites and companies, we strive to offer our services and communicate with our customers through various channels. Twitter, in particular, has become a favorite of ours as a useful “small” messaging service. We frequently tweet or retweet exciting, funny, or interesting content. We realize that you can’t follow every channel separately. After all, you have other things to do as well. That’s why we’ve integrated Twitter features into our website. You can follow our Twitter activity right here on the site or visit our Twitter page via a direct link. By integrating Twitter, we aim to enhance our service and improve the user experience on our website.
What data does Twitter store?
On some of our subpages, you’ll find built-in Twitter features. When you interact with Twitter content—such as by clicking a button—Twitter may collect and store data, even if you don’t have a Twitter account yourself. Twitter refers to this data as “log data.” This includes demographic data, browser cookie IDs, your smartphone’s ID, hashed email addresses, and information about which pages you’ve visited on Twitter and what actions you’ve taken. Of course, Twitter stores more data if you have a Twitter account and are logged in. This storage usually takes place via cookies. Cookies are small text files that are typically stored in your browser and transmit various types of information to Twitter.
We’ll now show you which cookies are set when you’re not logged into Twitter but visit a website with embedded Twitter features. Please consider this list an example. We cannot guarantee that it is exhaustive, as the selection of cookies is constantly changing and depends on your individual interactions with Twitter content.
These cookies were used in our test:
Name: personalization_id
Value: “v1_cSJIsogU51SeE122077330”
Purpose: This cookie stores information about how you use the website and which ads may have led you to Twitter.
Expiration date: after 2 years
Name: lang
Value: de
Purpose: This cookie stores your default or preferred language.
Expiration date: atthe end of the session
Name: guest_id
Value: 122077330v1%3A157132626
Purpose: This cookie is set to identify you as a guest.
Expiration date: after 2 years
Name: fm
Value: 0
Purpose: Unfortunately, we were unable to determine the purposeof this cookie.
Expiration date: atthe end of the session
Name: external_referer
Value: 1220773302beTA0sf5lkMrlGt
Purpose: This cookie collects anonymous data, such as how often you visit Twitter and how long you stay on Twitter.
Expiration date: After 6 days
Name: eu_cn
Value: 1
Purpose: This cookie tracks user activity and is used for various Twitter advertising purposes.
Expiration date: After one year
Name: ct0
Value: c1179f07163a365d2ed7aad84c99d966
Purpose: Unfortunately, we were unable to find any informationabout this cookie.
Expiration date: after 6 hours
Name: _twitter_sess
Value: 53D%253D–dd0248122077330-
Purpose: This cookie allows youto use features on the Twitter website.
Expiration date: at the end of the session
Note: Twitter also works with third-party providers. That is why we detected the three Google Analytics cookies—_ga, _gat, and _gid—during our test.
Twitter uses the data it collects, on the one hand, to better understand user behavior and thereby improve its own services and advertising offerings; on the other hand, the data is also used for internal security measures.
How long and where is the data stored?
When Twitter collects data from other websites, that data is deleted, aggregated, or otherwise anonymized after a maximum of 30 days. Twitter’s servers are located in various data centers in the United States. Accordingly, it can be assumed that the collected data is gathered and stored in the United States. Based on our research, we were unable to determine conclusively whether Twitter also has its own servers in Europe. In general, Twitter may store the collected data until it is no longer useful to the company, until you delete the data, or until a statutory retention period expires.
How can I delete my data or prevent it from being stored?
In its privacy policy, Twitter repeatedly emphasizes that it does not store any data from visits to external websites if you or your browser are located in the European Economic Area or Switzerland. However, if you interact directly with Twitter, Twitter will, of course, also store data about you.
If you have a Twitter account, you can manage your data by clicking “More” under the “Profile” button. Then click “Settings and Privacy.” Here, you can customize your data settings.
If you don't have a Twitter account, you can go to twitter.comand then click "Personalization." Under "Personalization and Data," you can manage the data that has been collected about you.
As mentioned above, most data is stored via cookies, which you can manage, disable, or delete in your browser. Please note that you can only “manage” cookies in the browser you have selected. This means that if you use a different browser in the future, you will need to manage your cookies there again according to your preferences. Under the “Cookies” section, you will find links to the relevant instructions for the most popular browsers.
You can also configure your browser to notify you each time a cookie is set. That way, you can always decide on a case-by-case basis whether to accept a cookie or not.
Twitter also uses this data for personalized ads both on and off Twitter. You can turn off personalized ads in your settings under “Personalization and Data.” If you use Twitter on a browser, you can disable personalized ads at https://optout.aboutads.info/?c=2&lang=EN.
Legal Basis
If you have consented to the processing and storage of your data through embedded social media elements, this consent serves as the legal basis for data processing (Art. 6(1)(a) GDPR). In general, your data is also stored and processed based on our legitimate interest (Art. 6(1)(f) GDPR) in maintaining prompt and effective communication with you or other customers and business partners. However, we only use the embedded social media elements to the extent that you have given your consent. Most social media platforms also set cookies in your browser to store data. Therefore, we recommend that you carefully read our privacy policy regarding cookies and review the privacy policy or cookie guidelines of the respective service provider.
Twitter processes your data in the United States, among other places. Please note that, in the opinion of the European Court of Justice, there is currently no adequate level of protection for data transfers to the United States. This may entail various risks regarding the lawfulness and security of data processing.
Twitter uses so-called Standard Contractual Clauses (Art. 46, paras. 2 and 3 of the GDPR) as the basis for data processing by recipients located in third countries (outside the European Union, Iceland, Liechtenstein, and Norway—specifically, the United States) or for data transfers to those countries. Standard Contractual Clauses (SCCs) are model templates provided by the European Commission and are intended to ensure that your data complies with European data protection standards even when it is transferred to and stored in third countries (such as the United States). Through these clauses, Twitter commits to adhering to European data protection standards when processing your relevant data, even if the data is stored, processed, and managed in the United States. These clauses are based on an implementing decision by the European Commission. You can find the decision and the corresponding Standard Contractual Clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
For more information about Twitter's Standard Contractual Clauses, visit https://gdpr.twitter.com/en/controller-to-controller-transfers.html.
We hope we have provided you with a general overview of how Twitter processes data. We do not receive any data from Twitter, nor are we responsible for what Twitter does with your data. If you have any further questions on this topic, we recommend that you review Twitter’s Privacy Policy at https://twitter.com/de/privacy.
Cloud Services
| Cloud Services Privacy Policy Summary 👥 Data Subjects: We, as the website operator, and you, as the website visitor 🤝 Purpose: Security and data storage 📓 Processed Data: Data such as your IP address, name, or technical data such as browser version You can find more details below and in the individual privacy policies or in the providers’ privacy statements 📅 Retention Period: In most cases, the data is stored until it is no longer needed to fulfill the service ⚖️ Legal basis: Art. 6(1)(a) GDPR (Consent), Art. 6(1)(f) GDPR (Legitimate Interests) |
What are cloud services?
Cloud services provide us, as website operators, with storage space and computing power via the Internet. Data can be transferred to an external system, processed, and stored via the Internet. The respective cloud provider manages this data. Depending on requirements, an individual or a company can choose the amount of storage space or computing power. Cloud storage is accessed via an API or storage protocols. API stands for Application Programming Interface, which refers to a programming interface that connects software and hardware components.
Why do we use cloud services?
We use cloud services for several reasons. A cloud service allows us to store our data securely. It also gives us access to the data from various locations and devices, providing us with greater flexibility and streamlining our work processes. Cloud storage also saves us money because we don’t have to set up and manage our own infrastructure for data storage and security. By storing our data centrally in the cloud, we can also expand our areas of application and manage our information much more effectively.
As website operators and as a company, we primarily use cloud services for our own purposes. For example, we use these services to manage our calendar and to store documents or other important information in the cloud. However, this may also involve the storage of your personal data. This is the case, for example, when you provide us with your contact information (such as your name and email address) and we store our customer data with a cloud provider. Consequently, data we process from you may also be stored and processed on external servers. When we offer certain forms or content from cloud services on our website, cookies may also be set for web analytics and advertising purposes. Furthermore, these cookies remember your settings (such as the language you use) so that you’ll find your familiar web environment the next time you visit our website.
What data is processed by cloud services?
Much of the data we store in the cloud is not personally identifiable; however, some data qualifies as personal data under the definition of the GDPR. This often includes customer data such as name, address, IP address, or phone number, or technical device information. Videos, images, and audio files can also be stored in the cloud. Exactly how the data is collected and stored depends on the specific service. We try to use only services that handle data in a highly trustworthy and professional manner. In general, services such as Amazon Drive have access to the stored files in order to provide their own services accordingly. To do so, however, these services require permissions—such as the right to copy files for security reasons. This data is processed and managed within the scope of the services and in compliance with applicable laws. This includes compliance with the GDPR for U.S. providers (via the Standard Contractual Clauses). In some cases, these cloud services also collaborate with third-party providers who may process data under instruction and in accordance with privacy policies and additional security measures. We would like to emphasize once again that all well-known cloud services (such as Amazon Drive, Google Drive, or Microsoft OneDrive) reserve the right to access stored content in order to provide and optimize their own services accordingly.
Duration of Data Processing
We provide information below regarding the duration of data processing, to the extent that we have further details on this matter. In general, cloud services store data until you or we revoke consent for data storage or delete the data. Generally, personal data is stored only for as long as is strictly necessary to provide the services. However, permanently deleting data from the cloud can take several months. This is because the data is usually not stored on just one server but is distributed across various servers.
Right to Object
You also have the right and the option to revoke your consent to data storage in the cloud at any time. If cookies are used, you also have the right to revoke your consent in this regard. You can do this either through our cookie management tool or through other opt-out features. For example, you can also prevent data collection via cookies by managing, disabling, or deleting cookies in your browser. We also recommend that you review our general privacy policy regarding cookies. To find out exactly which of your data is stored and processed, you should read the privacy policies of the respective cloud providers.
Legal Basis
We use cloud services primarily based on our legitimate interests (Art. 6(1)(f) of the GDPR) in having a robust security and storage system.
Certain processing activities, in particular the use of cookies and storage functions, require your consent. If you have consented to the processing and storage of your data by cloud services, this consent serves as the legal basis for data processing (Art. 6(1)(a) GDPR). Most of the services we use place cookies in your browser to store data. We therefore recommend that you carefully read our privacy policy regarding cookies and review the privacy policy or cookie policy of the respective service provider.
Information about specific tools—if available—can be found in the following sections.
Dropbox Privacy Policy
We use Dropbox, an online storage service for files, photos, and videos, for our website. The service provider is the American company Dropbox Inc. The company's European branch is located in Ireland (One Park Place, Floor 5, Upper Hatch Street, Dublin 2).
Dropbox processes your data in the United States, among other places. Please note that, in the opinion of the European Court of Justice, there is currently no adequate level of protection for data transfers to the United States. This may entail various risks regarding the lawfulness and security of data processing.
Dropbox uses so-called Standard Contractual Clauses (Art. 46, paras. 2 and 3 of the GDPR) as the legal basis for data processing by recipients located in third countries (outside the European Union, Iceland, Liechtenstein, and Norway—specifically, in the United States) or for data transfers to those countries. Standard Contractual Clauses (SCCs) are model clauses provided by the European Commission and are intended to ensure that your data continues to comply with European data protection standards even when it is transferred to and stored in third countries (such as the United States). Through these clauses, Dropbox commits to adhering to European data protection standards when processing your relevant data, even if the data is stored, processed, and managed in the United States. These clauses are based on an implementing decision by the European Commission. You can find the decision and the corresponding Standard Contractual Clauses here: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
The Data Processing Agreements, which are based on the Standard Contractual Clauses, can be found at https://assets.dropbox.com/documents/en/legal/dfb-data-processing-agreement.pdf.
For more information about the data processed when you use Dropbox, please see the Privacy Policy at https://www.dropbox.com/privacy.
Online Map Services: Introduction
| Online Map Services Privacy Policy Summary 👥 Data Subjects: Visitors to the website 🤝 Purpose: To improve the user experience 📓 Data Processed: The specific data processed depends heavily on the services used. In most cases, this includes IP addresses, location data, search terms, and/or technical data. You can find more details in the documentation for each tool used. 📅 Retention period: Depends on the tools used ⚖️ Legal basis: Art. 6(1)(a) GDPR (Consent), Art. 6(1)(f) GDPR (Legitimate Interests) |
What are online map services?
As an additional service, we also use online map services on our website. Google Maps is probably the service you’re most familiar with, but there are also other providers that specialize in creating digital maps. These services allow us to display locations, route maps, or other geographic information directly on our website. Thanks to an integrated map service, you no longer need to leave our website to, for example, view directions to a location. To ensure the online map works on our website, map sections are embedded using HTML code. These services can display road maps, the Earth’s surface, or aerial and satellite images. When you use the embedded map feature, data is also transmitted to and stored by the tool being used. This data may include personal information.
Why do we use online map services on our website?
Generally speaking, our goal is to ensure you have a pleasant experience on our website. And, of course, your experience will only be pleasant if you can easily navigate our website and find all the information you need quickly and easily. That’s why we thought an online map system could significantly improve the service we offer on our website. Without leaving our website, you can use the map system to easily view directions, locations, and even points of interest. It’s also incredibly convenient that you can see at a glance where our headquarters are located, so you can find us quickly and easily. As you can see, there are simply many advantages, and we clearly view online map services on our website as an integral part of our customer service.
What data do online map services store?
When you open a page on our website that includes an online map feature, personal data may be transmitted to the respective service and stored there. In most cases, this involves your IP address, which can also be used to determine your approximate location. In addition to your IP address, data such as search terms you’ve entered and longitude and latitude coordinates are also stored. For example, if you enter an address for route planning, this data is also stored. The data is not stored by us, but on the servers of the integrated tools. You can think of it this way: Although you are on our website, when you interact with a map service, that interaction actually takes place on their website. To ensure the service functions properly, at least one cookie is usually set in your browser. Google Maps, for example, also uses cookies to track user behavior so it can optimize its own service and display personalized ads. You can learn more about cookies in our “Cookies” section.
How long and where is the data stored?
Each online map service processes different types of user data. If we have additional information, we will provide details on the duration of data processing below in the relevant sections for each tool. As a general rule, personal data is only retained for as long as is necessary to provide the service. Google Maps, for example, stores certain data for a specified period of time, while you must delete other data yourself. With Mapbox, for instance, the IP address is retained for 30 days and then deleted. As you can see, each tool stores data for different lengths of time. We therefore recommend that you carefully review the privacy policies of the tools we use.
Providers also use cookies to store data about your usage of the map service. You can find more general information about cookies in our “Cookies” section, but you can also learn which cookies may be used by reviewing the privacy policies of the individual providers. In most cases, however, these are only illustrative lists and are not exhaustive.
Right to Object
You always have the option and the right to access your personal data and to object to its use and processing. You may also revoke the consent you have given us at any time. Generally, the easiest way to do this is through the cookie consent tool. However, there are also other opt-out tools you can use. You can also manage, delete, or disable any cookies set by the providers we use with just a few clicks. However, this may cause some features of the service to no longer function as usual. How you manage cookies in your browser depends on which browser you’re using. In the “Cookies” section, you’ll also find links to the instructions for the most popular browsers.
Legal Basis
If you have consented to the use of an online map service, that consent serves as the legal basis for the corresponding data processing. Pursuant to Article 6(1)(a) of the GDPR (Consent), this consent constitutes the legal basis for the processing of personal data, such as that which may occur when data is collected by an online map service.
We also have a legitimate interest in using an online map service to optimize the service on our website. The legal basis for this is Article 6(1)(f) of the GDPR (Legitimate Interests). However, we only use an online map service if you have given your consent. We want to make absolutely clear once again at this point.
Information about specific online map services—if available—can be found in the following sections.
Miscellaneous: Introduction
| Miscellaneous Privacy Policy Summary 👥 Data Subjects: Visitors to the website 🤝 Purpose: Improving the user experience 📓 Data Processed: The specific data processed depends heavily on the services used. In most cases, this includes IP addresses and/or technical data. You can find more details in the descriptions of the respective tools used. 📅 Retention period: Depends on the tools used ⚖️ Legal basis: Art. 6(1)(a) GDPR (Consent), Art. 6(1)(f) GDPR (Legitimate Interests) |
What falls under “Other”?
The “Other” category includes services that do not fit into any of the categories listed above. These are generally various plugins and embedded elements that enhance our website. These features are generally sourced from third-party providers and integrated into our website. Examples include web search services such as Algolia Place, Giphy, and Programmable Search Engine, as well as online services for weather data such as OpenWeather.
Why do we use other third-party providers?
Through our website, we aim to offer you the best online experience in our industry. A website has long since ceased to be merely a business card for companies. Rather, it is a place designed to help you find what you’re looking for. To continually make our website even more interesting and helpful for you, we use various third-party services.
What data is processed?
Whenever elements are integrated into our website, your IP address is transmitted to the respective provider, stored, and processed there. This is necessary because otherwise the content would not be sent to your browser and, consequently, would not be displayed properly. Service providers may also use pixel tags or web beacons. These are small graphics on websites that can record a log file and generate analyses of that file. Providers can use the information obtained to improve their own marketing efforts. In addition to pixel tags, such information (such as which button you click or when you visit a particular page) may also be stored in cookies. These cookies may contain not only analytical data about your web behavior but also technical information, such as your browser type or operating system. Some providers may also link the collected data to other internal services or to third-party providers. Each provider handles your data differently. Therefore, we recommend that you carefully read the privacy policies of the respective services. As a general rule, we strive to use only services that handle data protection with the utmost care.
Duration of Data Processing
We provide information below regarding the duration of data processing, to the extent that we have further details on this matter. In general, we process personal data only for as long as is strictly necessary to provide our services and products.
Legal Basis
If we ask for your consent and you agree to allow us to use the service, this serves as the legal basis for the processing of your data (Art. 6(1)(a) GDPR). In addition to your consent, we have a legitimate interest in analyzing the behavior of website visitors in order to improve our services both technically and economically. The legal basis for this is Article 6(1)(f) of the GDPR (legitimate interests). However, we only use these tools to the extent that you have given your consent.
Information about the specific tools—if available—can be found in the following sections.
Weglot Privacy Policy
We use the Weglot translation service for our website. The service provider is the French company Weglot SAS, located at 7 Cité Paradis, 75010 Paris, France.
For more information about the data processed through the use of Weglot, please see the Privacy Policy at https://weglot.com/privacy/.
Explanation of Terms Used
We always strive to make our Privacy Policy as clear and understandable as possible. However, this isn’t always easy, especially when it comes to technical and legal topics. It often makes sense to use legal terms (such as “personal data”) or certain technical terms (such as “cookies” and “IP address”). However, we do not want to use these terms without providing an explanation. Below, you will find an alphabetical list of important terms we use that we may not have addressed sufficiently in the privacy policy so far. If these terms are taken from the GDPR and are definitions, we will also cite the relevant GDPR text here and, where appropriate, add our own explanations.
Data Processor
Definition pursuant to Article 4 of the GDPR
For the purposes of this regulation, the term “” means:
“Processor” means a natural or legal person, public authority, agency, or other body that processes personal data on behalf of the controller;
Explanation: As a company and website owner, we are responsible for all data we process from you. In addition to the data controllers, there may also be so-called data processors. This includes any company or individual that processes personal data on our behalf. Data processors may therefore include, in addition to service providers such as tax advisors, hosting or cloud providers, payment or newsletter providers, or large companies such as Google or Microsoft.
Consent
Definition pursuant to Article 4 of the GDPR
For the purposes of this regulation, the term “” means:
“Consent” of the data subject means any freely given, specific, informed, and unambiguous indication of the data subject’s wishes, expressed in the form of a statement or other unambiguous affirmative action, by which the data subject indicates that he or she consents to the processing of personal data relating to him or her;
Explanation: On websites, this type of consent is typically obtained through a cookie consent tool. You’re probably familiar with it. Whenever you visit a website for the first time, you’re usually asked via a banner whether you agree to or consent to data processing. In most cases, you can also configure individual settings and thus decide for yourself which data processing you allow and which you do not. If you do not give your consent, no personal data about you may be processed. In principle, consent can of course also be given in writing—that is, not via a tool.
Personal Data
Definition pursuant to Article 4 of the GDPR
For the purposes of this regulation, the term “” means:
“personal data” any information relating to an identified or identifiable natural person (hereinafter referred to as the “data subject”); A natural person is considered identifiable if they can be identified, directly or indirectly, in particular by association with an identifier such as a name, an identification number, location data, an online identifier, or one or more specific characteristics that reflect the physical, physiological, genetic, mental, economic, cultural, or social identity of that natural person;
Explanation: Personal data is any information that can be used to identify you as an individual. This typically includes information such as:
- Name
- Address
- Email address
- Mailing Address
- Phone number
- Date of Birth
- Identification numbers such as Social Security number, tax identification number, ID card number, or student ID number
- Banking information such as account numbers, credit information, account balances, and much more.
According to the European Court of Justice (ECJ), your IP address is also considered personal data. IT experts can use your IP address to determine at least the approximate location of your device and, subsequently, identify you as the account holder. Therefore, storing an IP address also requires a legal basis under the GDPR. There are also so-called “special categories” of personal data that require special protection. These include:
- Racial and Ethnic Origin
- political views
- religious or ideological beliefs
- union membership
- genetic data, such as data obtained from blood or saliva samples
- Biometric data (information about psychological, physical, or behavioral characteristics that can identify a person).
Health data - Data on sexual orientation or sex life
Profiling
Definition pursuant to Article 4 of the GDPR
For the purposes of this regulation, the term “” means:
“Profiling” means any form of automated processing of personal data that consists of using such personal data to evaluate certain personal aspects relating to a natural person, in particular to analyze or predict aspects concerning that natural person’s work performance, economic situation, health, personal preferences, interests, reliability, behavior, location, or movements;
Explanation: Profiling involves gathering various pieces of information about a person in order to learn more about that person. On the web, profiling is often used for advertising purposes or for credit checks. For example, web or advertising analytics programs collect data about your behavior and interests on a website. This results in a specific user profile, which can be used to deliver targeted advertising to a specific audience.
Person in Charge
Definition pursuant to Article 4 of the GDPR
For the purposes of this regulation, the term “” means:
“Controller” means the natural or legal person, public authority, agency, or other body that, alone or jointly with others, determines the purposes and means of the processing of personal data; where the purposes and means of such processing are determined by Union law or the law of the Member States, the controller or the specific criteria for its designation may be provided for by Union law or the law of the Member States;
Explanation: In our case, we are responsible for processing your personal data and are therefore the “data controller.” If we transfer collected data to other service providers for processing, those providers are “data processors.” A “Data Processing Agreement (DPA)” must be signed for this purpose.
Processing
Definition pursuant to Article 4 of the GDPR
For the purposes of this regulation, the term “” means:
“Processing” any operation or set of operations performed on personal data, whether or not by automated means, such as collection, recording, organization, structuring, storage, adaptation or alteration, retrieval, consultation, use, disclosure by transmission, distribution, or any other form of disclosure, the matching or linking, the restriction, erasure, or destruction;
Note: When we refer to “processing” in our Privacy Policy, we mean any type of data processing. As mentioned above in the original GDPR statement, this includes not only the collection but also the storage and processing of data.
All texts are protected by copyright.
Table of Contents
- Privacy Policy: Introduction and Overview
- Scope
- Legal Bases
- Contact information for the data controller
- Contact information for our data protection officer
- Storage Period
- Rights under the General Data Protection Regulation
- Data transfers to third countries
- Security of Data Processing Operations
- Communications
- Data Processing Agreement (DPA)
- Cookies
- Customer Data
- Registration
- Web hosting
- Web Analytics
- Email Marketing
- Social Media
- Cloud Services
- Introduction to Online Map Services
- Miscellaneous Overview
- Explanation of the terminology used
Privacy Policy: Introduction and Overview
We have written this privacy policy (version September 27, 2023-122077330) to explain to you, in accordance with the provisions of the General Data Protection Regulation (EU) 2016/679 and applicable national laws, which personal data (referred to as “data” for short) we, as the data controller—and the data processors commissioned by us (e.g., service providers)—process, will process in the future, and what legal options you have. The terms used are to be considered gender-neutral.
In short: We provide you with comprehensive information about any of your personal data that we process.
Privacy policies usually sound very technical and use legal terminology. However, this privacy policy is intended to describe the most important information for you as simply and transparently as possible. To promote transparency, technical terms are explained in a reader-friendly manner, links to additional information are provided, and graphics are used. We are therefore stating in clear and simple language that we only process personal data in the course of our business activities if there is a legal basis for doing so. This certainly cannot be achieved with brief, unclear, and overly technical legal statements, as is often the norm on the internet when it comes to data protection. I hope you find the following explanations interesting and informative. Perhaps you will also discover some information that was previously new to you.
If you still have questions, we kindly ask you to contact the responsible body named below or in the legal notice, follow the provided links, and review additional information on third-party websites. You can, of course, also find our contact details in the legal notice.
Scope
This privacy policy applies to all personal data processed by our company and to all personal data processed by companies we have contracted (processors). The term “personal data” refers to information as defined in Article 4(1) of the GDPR, such as a person’s name, email address, and mailing address. The processing of personal data enables us to offer and invoice our services and products, whether online or offline. The scope of this privacy policy includes:
- all of our online platforms (websites, online stores) that we operate
- Social media presence and email communication
- mobile apps for smartphones and other devices
In short: This privacy policy applies to all areas in which the company processes personal data in a structured manner through the channels mentioned. Should we enter into a legal relationship with you outside of these channels, we will notify you separately if necessary.
Legal Bases
In the following privacy policy, we provide you with transparent information on the legal principles and regulations—that is, the legal bases under the General Data Protection Regulation—that enable us to process personal data.
Whenever EU law is concerned, we refer to REGULATION (EU) 2016/679 OF THE EUROPEAN PARLIAMENT AND OF THE COUNCIL of April 27, 2016. You can, of course, access the EU’s General Data Protection Regulation online at EUR-Lex, the gateway to EU law, at https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=celex%3A32016R0679.
We process your data only if at least one of the following conditions applies:
- Consent (Article 6, Paragraph 1, subparagraph (a) of the GDPR): You have given us your consent to process data for a specific purpose. An example would be the storage of data you entered into a contact form.
- Contract (Article 6, Paragraph 1, subparagraph (b) of the GDPR): We process your data in order to fulfill a contract or pre-contractual obligations with you. For example, if we enter into a sales contract with you, we need personal information in advance.
- Legal obligation (Article 6, Paragraph 1, subparagraph (c) of the GDPR): If we are subject to a legal obligation, we will process your data. For example, we are legally required to retain invoices for our bookkeeping. These invoices typically contain personal data.
- Legitimate interests (Article 6(1)(f) of the GDPR): In cases where legitimate interests do not infringe upon your fundamental rights, we reserve the right to process personal data. For example, we must process certain data in order to operate our website securely and cost-effectively. Therefore, such processing constitutes a legitimate interest.
Other conditions, such as recording for the public interest, the exercise of official authority, and the protection of vital interests, do not typically apply in our case. Should such a legal basis be relevant, it will be disclosed in the appropriate place.
In addition to the EU regulation, national laws also apply:
- In Austria, this is the Austrian Data Protection Act (Datenschutzgesetz), or DSG for short.
- In Germany, this is the Federal Data Protection Act (Bundesdatenschutzgesetz), or BDSG for short.
If other regional or national laws apply, we will provide you with information about them in the following sections.
Contact information for the data controller
If you have any questions about data protection, you will find the contact details of the responsible person or controller below:
Langer GmbH
Steyrerstrasse 13, 4470 Enns
Austria
Authorized representative: Fritz Aichhorn
Email: fritz@langer-magnet.com
Phone: +43 7223 82592-0
Company details: https://www.langer-magnet.com/impressum/
Contact information for our data protection officer
You can find the contact information for our data protection officer below:
Email: fritz@langer-magnet.com
Phone: +43 664 2324180
Storage Period
It is our general policy to retain personal data only for as long as is absolutely necessary to provide our services and products. This means that we delete personal data as soon as there is no longer any reason to process it. In some cases, we are legally required to retain certain data even after the original purpose no longer exists, such as for accounting purposes.
If you want your data to be deleted or if you want to revoke your consent to data processing, the data will be deleted as soon as possible, provided there is no obligation to continue storing it.
We will provide details below regarding the specific duration of the respective data processing, provided we have further information.
Rights under the General Data Protection Regulation
In accordance with Articles 13 and 14 of the GDPR, we are informing you of the following rights you have to ensure fair and transparent data processing:
- According to Article 15 of the GDPR, you have the right to know whether we are processing data about you. If we are, you have the right to receive a copy of the data and to know the following information:
- for what purpose we are processing;
- the categories, i.e., the types of data that are processed;
- who receives this data and, if the data is transferred to third countries, how security can be ensured;
- how long the data will be stored;
- the existence of the right to rectification, erasure, or restriction of processing, and the right to object to processing;
- that you can file a complaint with a supervisory authority (links to these authorities can be found below);
- the source of the data if we did not collect it from you;
- Whether profiling is performed, i.e., whether data is automatically analyzed to create a personal profile of you.
- You have the right to have your data rectified under Article 16 of the GDPR, which means that we must correct any errors you find in your data.
- You have the right to erasure (“right to be forgotten”) under Article 17 of the GDPR, which specifically means that you may request the deletion of your data.
- According to Article 18 of the GDPR, you have the right to restrict processing, which means that we may only store the data but not use it further.
- According to Article 20 of the GDPR, you have the right to data portability, which means that we will provide you with your data in a standard format upon request.
- According to Article 21 of the GDPR, you have the right to object, which results in a change in how your data is processed once the objection is enforced.
- If the processing of your data is based on Article 6(1)(e) (public interest, exercise of official authority) or Article 6(1)(f) (legitimate interest), you may object to the processing. We will then determine as soon as possible whether we can legally comply with this objection.
- If data is used for direct marketing, you may object to this type of data processing at any time. We will then no longer use your data for direct marketing.
- If data is used for profiling, you may object to this type of data processing at any time. We will no longer use your data for profiling after that.
- According to Article 22 of the GDPR, you may have the right not to be subject to a decision based solely on automated processing (for example, profiling).
- You have the right to file a complaint under Article 77 of the GDPR. This means that you can file a complaint with the data protection authority at any time if you believe that the processing of personal data violates the GDPR.
In short: You have rights—don't hesitate to contact the responsible party listed above with us!
If you believe that the processing of your data violates data protection law or that your data protection rights have been violated in any other way, you can file a complaint with the supervisory authority. In Austria, this is the Data Protection Authority, whose website can be found at https://www.dsb.gv.at/. In Germany, there is a data protection officer for each federal state. For more information, you can contact the Federal Commissioner for Data Protection and Freedom of Information (BfDI). The following local data protection authority is responsible for our company:
Austrian Data Protection Authority
Manager: Mag . Dr. Andrea Jelinek
Address: Barichgasse 40-42, 1030 Vienna
Phone number: +43 1 52 152-0
Email address: dsb@dsb.gv.at
Website: https://www.dsb.gv.at/
Data transfers to third countries
We only transfer or process data to countries outside the EU (third countries) if you consent to such processing, if it is required by law, or if it is contractually necessary. In any case, we generally do so only to the extent permitted by law. In most cases, your consent is the primary basis for processing data in third countries. When personal data is processed in third countries such as the United States—where many software providers offer their services and host their servers—your personal data may be processed and stored in unexpected ways.
We would like to expressly point out that, according to the European Court of Justice, there is currently no adequate level of protection for data transfers to the United States. Data processing by U.S. services (such as Google Analytics) may result in data being processed and retained without having undergone anonymization processes. Furthermore, U.S. government authorities may be able to access individual data. The collected data may also be linked to data from other services provided by the same provider, should you have a user account with that provider. We strive to use server locations within the EU whenever this is offered and possible.
We will provide you with more details about data transfers to third countries in the relevant sections of this privacy policy, whenever applicable.
Security of Data Processing Operations
To protect personal data, we have implemented both technical and organizational measures. We encrypt or pseudonymize personal data whenever possible. In this way, we make it as difficult as possible for third parties to extract personal information from our data.
Article 25 of the GDPR refers to “data protection by design and by default,” which means that appropriate safeguards and security measures must always be in place for both software (e.g., forms) and hardware (e.g., access to server rooms). Where applicable, we will outline the specific measures below.
TLS encryption with HTTPS
The terms TLS, encryption, and HTTPS sound very technical—and they certainly are. We use HTTPS (Hypertext Transfer Protocol Secure) to securely transfer data over the Internet.
This means that the entire transmission of all data from your browser to our web server is secured—no one can “eavesdrop.”
We have thus added an additional layer of security and met privacy requirements through our technology design Article 25, Section 1 of the GDPR). By using TLS (Transport Layer Security), an encryption protocol designed to ensure secure data transfer over the Internet, we can ensure the protection of confidential information.
You can tell that this security feature is in use by the small lock icon  , which is located in the top-left corner of your browser to the left of the web address (e.g., examplepage.uk), as well as by the presence of the letters "https" (instead of "http") as part of our web address.
If you want to learn more about encryption, we recommend that you do a Google search for “Hypertext Transfer Protocol Secure wiki” to find useful links to additional information.
Communications
| Communications Overview 👥 Affected parties: Anyone who communicates with us via phone, email, or online form 🤝 Data processed: e.g., phone number, name, email address, or data entered in forms. You can find more details on this under the respective contact form 📓 Purpose: handling communication with customers, business partners, etc. 📅 Retention period: for the duration of the business relationship and as required by law ⚖️ Legal basis: Article 6(1)(a) of the GDPR (consent), Article 6(1)(b) of the GDPR (contract), Article 6(1)(f) of the GDPR (legitimate interests) |
If you contact us and communicate with us by phone, email, or online form, your personal data may be processed.
The data will be processed to handle and process your request and for the related business transaction. The data is stored for this period of time or for as long as required by law.
Affected individuals
The processes mentioned above affect everyone who contacts us through the communication channels we provide.
Telephone
When you call us, the call data is stored in a pseudonymized form on the respective device, as well as by the telecommunications provider being used. In addition, data such as your name and phone number may be sent via email and stored for the purpose of responding to your inquiries. The data will be deleted as soon as the business matter has been resolved and legal requirements permit its deletion.
If you communicate with us via email, your data is stored on the respective device (computer, laptop, smartphone, etc.) as well as on the email server. The data will be deleted as soon as the business matter has been resolved and legal requirements permit its deletion.
Online forms
If you contact us using an online form, your data is stored on our web server and, if necessary, forwarded to our email address. The data will be deleted as soon as the business matter has been resolved and legal requirements permit its deletion.
Legal Bases
Data processing is based on the following legal grounds:
- Art. 6, para. 1, subpar. a of the GDPR (consent): You give us your consent to store your data and to continue using it for the purposes of the business case;
- Art. 6, para. 1, subparagraph b of the GDPR (contract): For the performance of a contract with you or a processor, such as a telephone provider, or if we need to process the data for pre-contractual activities, such as preparing an offer;
- Art. 6, para. 1, subpara. f of the GDPR (legitimate interests): We want to handle our customer inquiries and business communications in a professional manner. Therefore, certain technical tools—such as email programs, Exchange servers, and mobile network operators—are necessary to efficiently manage our communications.
Data Processing Agreement (DPA)
In this section, we would like to explain what a Data Processing Agreement is and why it is needed. Since the term “Data Processing Agreement” is quite long, we will often use only the acronym DPA in this text. Like most companies, we do not work alone but also use the services of other companies or individuals. By engaging different companies or service providers, we may transfer personal data to them for processing. These partners then act as data processors with whom we enter into a contract, known as a Data Processing Agreement (DPA). The most important thing for you to know is that any processing of your personal data takes place exclusively in accordance with our instructions and must be governed by the DPA.
Who are the data processors?
As a company and website owner, we are responsible for any of your data that we process. In addition to the controller, there may also be so-called processors involved. This includes any company or person who processes your personal data. More precisely, and according to the GDPR’s definition, this means: Any natural or legal person, public authority, agency, or other body that processes your personal data is considered a processor. Processors can therefore be service providers such as hosting or cloud providers, payment or newsletter providers, or large companies such as Google or Microsoft.
To make the terminology easier to understand, here is an overview of the three roles under the GDPR:
Data subject (you as a customer or interested party) → Controller(we as a company and contracting entity) → Processors (service providers such as web hosts or cloud providers)
Contents of a Data Processing Agreement
As mentioned above, we have entered into a DPA with our partners who act as data processors. First and foremost, it stipulates that the data processor must process the data exclusively in accordance with the GDPR. The contract must be concluded in writing, although an electronic contract is also considered a “written contract.” Any processing of personal data may only take place after this contract has been concluded. The contract must include the following:
- notification to us as the data controller
- Obligations and Rights of the Data Controller
- categories of data subjects
- type of personal data
- Type and Purpose of Data Processing
- Subject and Duration of Data Processing
- location of data processing
Furthermore, the contract sets forth all of the processor's obligations. The most important obligations are:
- ensuring data security measures
- taking appropriate technical and organizational measures to protect the rights of the data subject
- maintaining a data processing record
- cooperation with the data protection authority upon request
- conducting a risk analysis for any personal data received
- Subprocessors may be appointed only with the written consent of the controller
You can see an example of what a DPA looks like at https://gdpr.eu/data-processing-agreement/. This link shows a sample contract.
Cookies
| Cookies Overview 👥 Affected parties: visitors to the website 🤝 Purpose: depends on the specific cookie. You can find more details below or from the software manufacturer that sets the cookie. 📓 Processed data: depends on the cookie used. More details can be found below or from the manufacturer of the software that sets the cookie. 📅 Storage duration: can vary from hours to years, depending on the respective cookie ⚖️ Legal basis: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are cookies?
Our website uses HTTP cookies to store user-specific data.
Below, we explain what cookies are and why they are used, so that you can better understand the privacy policy that follows.
Whenever you browse the Internet, you are using a browser. Common browsers include Chrome, Safari, Firefox, Internet Explorer, and Microsoft Edge. Most websites store small text files in your browser. These files are called cookies.
It is important to note that cookies are very useful little helpers. Almost every website uses cookies. More precisely, these are HTTP cookies, as there are also other types of cookies for other purposes. HTTP cookies are small files that our website stores on your computer. These cookie files are automatically placed in the cookie folder, which is the “brain” of your browser. A cookie consists of a name and a value. Furthermore, to define a cookie, one or more attributes must be specified.
Cookies store certain user data about you, such as your language or personal page settings. When you return to our website, your browser sends this “user-related” information back to our site. Thanks to cookies, our website recognizes you and provides you with the settings you’re familiar with. In some browsers, each cookie has its own file, while in others—such as Firefox—all cookies are stored in a single file.
The following graphic illustrates a possible interaction between a web browser, such as Chrome, and the web server. The web browser requests a website and receives a cookie from the server in response. The browser then uses this cookie again as soon as another page is requested.

There are both first-party cookies and third-party cookies. First-party cookies are created directly by our site, while third-party cookies are created by partner websites (e.g., Google Analytics). Each cookie must be evaluated individually, as each cookie stores different data. The expiration time of a cookie also varies from a few minutes to a few years. Cookies are not software programs and do not contain viruses, Trojans, or other malware. Cookies also cannot access information on your computer.
Here is an example of what cookie files might look like:
Name: _ga
Value: GA1.2.1326744211.152122077330-9
Purpose: To distinguish between website visitors
Expiration date: after 2 years
A browser should support these minimum sizes:
- At least 4,096 bytes per cookie
- At least 50 cookies per domain
- At least 3,000 cookies in total
What types of cookies are there?
The specific cookies we use depend on the services we utilize, which will be described in the following sections of this privacy policy. First, we will briefly discuss the different types of HTTP cookies.
There are 4 different types of cookies:
Essential cookies
These cookies are necessary to ensure the basic functions of a website. They are needed, for example, when a user adds a product to their shopping cart, then continues browsing other websites, and returns later to proceed to checkout. These cookies ensure that the shopping cart is not deleted, even if the user closes their browser window.
Purpose-based cookies
These cookies collect information about user behavior and whether the user receives any error messages. In addition, these cookies track the website’s loading time as well as its performance across different browsers.
Targeted cookies
These cookies improve the user experience. As a result, information such as previously entered locations, font sizes, or data in forms remains stored.
Advertising cookies
These cookies are also known as targeting cookies. They are used to deliver personalized advertisements to the user. This can be very useful, but also quite annoying.
When you visit a website for the first time, you are usually asked which of these types of cookies you want to accept. Furthermore, this decision will, of course, also be stored in a cookie.
If you want to learn more about cookies and don't mind reading technical documentation, we recommend https://tools.ietf.org/html/rfc6265, the Internet Engineering Task Force (IETF) Request for Comments titled “HTTP State Management Mechanism.”
Purpose of Processing via Cookies
The purpose ultimately depends on the specific cookie. You can find more details below or from the software manufacturer that sets the cookie.
What data is processed?
Cookies are little helpers that perform a wide variety of tasks. Unfortunately, it is not possible to say exactly what data is generally stored in cookies, but in the privacy policy below, we will inform you about what data is processed or stored.
Cookie retention period
The storage period depends on the specific cookie and is described in more detail below. Some cookies are deleted in less than an hour, while others can remain on a computer for several years.
You can also control the storage duration yourself. You can manually delete all cookies at any time in your browser (see also “Right to Object” below). Furthermore, cookies based on consent will be deleted at the latest when you withdraw your consent. The legality of their storage will remain unaffected until then.
Right to object – how can I delete cookies?
You can decide for yourself how and whether you want to use cookies. Regardless of which service or website the cookies come from, you always have the option to delete, disable, or accept only some cookies. For example, you can block third-party cookies but allow all other cookies.
If you want to find out which cookies have been stored in your browser, or if you want to change or delete cookie settings, you can find this option in your browser settings:
Chrome: Clear, enable, and manage cookies in Chrome
Safari: Manage cookies and website data in Safari
Firefox: Clear cookies and site data in Firefox
Internet Explorer: Delete and manage cookies
Microsoft Edge: Delete cookies in Microsoft Edge
If you generally do not want cookies, you can configure your browser to notify you whenever a cookie is about to be set. This allows you to manually decide whether to allow or block each individual cookie. The procedure varies depending on the browser. Therefore, it might be best for you to search for instructions on Google. If you are using Chrome, for example, you could enter the search terms “delete cookies Chrome” or “disable cookies Chrome” into Google.
Legal basis
The so-called “Cookie Directive” has been in effect since 2009. It stipulates that the storage of cookies requires your consent (Article 6, Paragraph 1, subparagraph a of the GDPR). Within EU member states, however, responses to these guidelines still vary widely. In Austria, however, this directive was implemented in Section 96(3) of the Telecommunications Act (TKG). In Germany, the cookie guidelines have not been implemented as national law. Instead, these guidelines were largely implemented in Section 15(3) of the Telemedia Act (TMG).
For cookies that are absolutely necessary, even if consent has not been given, there are legitimate interests (Article 6(1)(f) of the GDPR), which in most cases are of an economic nature. We want to provide our visitors with a pleasant user experience on our website. To do so, certain cookies are often absolutely necessary.
This is done exclusively with your consent, unless strictly necessary cookies are used. The legal basis for this is Article 6(1)(a) of the GDPR.
In the following sections, you will find more details about the use of cookies, provided that the software in question does use cookies.
Customer Data
| Customer Data Overview 👥Affected parties: Customers or business and contractual partners 🤝 Purpose: Performance of a contract for the provision of agreed services or prior to entering into such a contract, including associated communications. 📓 Data processed: name, address, contact details, email address, phone number, payment information (such as invoices and bank details), contract data (such as duration and subject matter of the contract), IP address, order data 📅 Retention period: The data will be deleted as soon as it is no longer required for our business purposes and there is no legal obligation to process it. ⚖️ Legal bases: Legitimate interests (Art. 6, para. 1, lit. f GDPR), Contract (Art. 6, para. 1, lit. b GDPR) |
What is customer data?
In order to provide our services and fulfill our contractual obligations, we also process data from our customers and business partners. This data always includes personal data. Customer data refers to all information processed on the basis of contractual or pre-contractual agreements for the purpose of providing the services we offer. Customer data therefore encompasses all the information we collect and process about our customers.
Why do we process customer data?
There are many reasons why we collect and process customer data. The main reason is that we simply need specific data to provide our services. Sometimes, for example, your email address may be sufficient. However, if you purchase a product or service, we may also need data such as your name, address, bank details, or other contract information. This data will subsequently be used for marketing and sales optimization so that we can improve our overall service for our customers and clients. Another important reason for processing data is our customer service, which is very important to us. We want you to be able to contact us at any time with questions about our offerings. Therefore, we may need certain information, such as your email address, at a minimum.
What data is processed?
The only way to show exactly which data is stored is to categorize it. Ultimately, it always depends on which of our services you use. In some cases, you may only provide us with your email address so that we can, for example, contact you or answer your questions. In other cases, you may purchase one of our products or services. In those cases, we may need significantly more information, such as your contact information, payment details, and contract details.
Here is a list of the types of data we may receive and process:
- Name
- Contact Address
- Email address
- Phone number
- Your birthday
- Payment data (invoices, bank information, payment history, etc.)
- Contract details (term, scope)
- Usage data (websites visited, access data, etc.)
- Metadata (IP address, device information)
How long is the data stored?
We delete the corresponding customer data as soon as we no longer need it to fulfill our contractual obligations and purposes, and as soon as the data is also no longer necessary for any warranty or liability obligations. This may be the case, for example, when a business contract ends. After that, the retention period is usually 3 years, although longer periods may apply in individual cases. Of course, we also comply with statutory retention requirements. Your customer data will certainly not be shared with third parties unless you have given your explicit consent.
Legal Basis
The legal basis for the processing of your data is Article 6(1)(a) of the GDPR (consent), Article 6(1)(b) of the GDPR (contract or pre-contractual measures), Article 6(1)(f) of the GDPR (legitimate interests), and, in special cases (e.g., medical services), Article 9(2) of the GDPR (processing of special categories of data).
In cases involving the protection of vital interests, data processing is carried out in accordance with Article 9(2)(c) of the GDPR. For the purposes of health care, occupational medicine, medical diagnostics, care, or treatment in the health or social sectors, or for the administration of systems and services in the health or social sectors, the processing of personal data is carried out in accordance with Article 9(2)(h) of the GDPR. If you voluntarily provide data falling under these special categories, the processing is carried out on the basis of Article 9(2)(a) of the GDPR.
Registration
| Registration Overview 👥 Affected parties: Anyone who registers to create an account with us and logs in to use the account. 📓 Processed data: Personal data such as email address, name, password, and other data collected during registration, login, and account use. 🤝 Purpose: To provide our services and to communicate with clients or customers in connection with our services. 📅 Retention period: As long as the company account associated with the texts exists, plus a period of typically 3 years. ⚖️ Legal bases: Article 6(1)(b) of the GDPR (contract), Article 6(1)(a) of the GDPR (consent), Article 6(1)(f) of the GDPR (legitimate interests) |
If you register with us and provide any personal data, this data may be processed, possibly along with your IP address. Below, you can learn more about what we mean by the rather broad term “personal data.”
Please enter only the information we need for registration. If you are registering on behalf of a third party, please enter only the information for which you have the consent of the person you are registering. If possible, use a strong password that you do not use anywhere else and an email address that you check regularly.
Below, we will explain exactly what kind of data processing we do. After all, we want you to feel comfortable with the services we provide!
What is a registration?
When you register, we retain certain information about you to make it easy for you to log in to our website and use your account. Having an account with us has the advantage that you don’t have to re-enter all your information every time. It saves time and effort and ultimately prevents any issues with the provision of our services.
Why do we process personal data?
In short, we process personal data to enable you to register for an account and use it. If we didn’t do this, you would have to enter all your information each time, wait for our approval, and then enter everything again. This tedious process would likely irritate not only us a little, but also many of our valued clients and customers.
What data is processed?
Any data you provided during registration or login, and any data you may enter as part of managing your account information.
During registration, we process the following types of data:
- First Name
- Last name
- Email address
- Company Name
- Street + house number
- Residence
- Postal Code
- Country
During registration, we process any data you enter—such as your username and password—as well as data collected in the background, such as your device information and IP addresses.
When you use your account, we process any data you enter while using the account, as well as any data generated while you use our services.
Storage time
We store the data you provide for at least as long as the account associated with that data remains active with us—and for as long as there are contractual obligations between you and us. If the contract ends, we retain the data until the respective claims become time-barred. Furthermore, we store your data for as long as we are subject to legal retention requirements, if applicable. After that, we retain any accounting records (invoices, contract documents, account statements, etc.) related to the contract for 10 years (§ 147 AO) and other relevant business documents for 6 years (§ 247 HGB) after they are created.
Right to Object
Have you registered, entered data, and now want to revoke consent for data processing? No problem. As you can see above, you retain this right under the General Data Protection Regulation even during and after registration, login, or account creation with us. Contact the Data Protection Officer listed above to exercise your rights. If you already have an account with us, you can easily view and manage your data and text in your account.
We use the “Real Cookie Banner” consent tool to manage the cookies and similar technologies (tracking pixels, web beacons, etc.) we use, as well as the related consents. You can find details on how “Real Cookie Banner” works at <a href=“https://devowl.io/de/rcb/datenverarbeitung/“ rel=“noreferrer“ target=“_blank“>https://devowl.io/de/rcb/datenverarbeitung/</a>.
The legal basis for the processing of personal data in this context is Article 6(1)(c) of the GDPR and Article 6(1)(f) of the GDPR. Our legitimate interest is the management of the cookies and similar technologies used and the related consents.
The provision of personal data is neither contractually required nor necessary for the conclusion of a contract. You are not obligated to provide personal data. If you do not provide personal data, we cannot manage your consents.
Translated with DeepL.com (free version)
Legal Basis
By completing the registration process, you enter into a pre-contractual agreement with us, with the intention of entering into a contract for the use of our platform (although there is no automatic payment obligation). You invest time in entering data and registering, and in return, we offer you our services once you log in to our system and view your customer account. We also fulfill our contractual obligations. Finally, we need to be able to email registered users about important changes. Article 6(1)(b) of the GDPR (implementation of pre-contractual measures, fulfillment of a contract) applies.
Where applicable, we will ask for your consent—for example, if you voluntarily provide more data than is absolutely necessary, or if we ask whether we may send you advertising. Article 6(1)(a) of the GDPR (consent) applies in this regard.
We also have a legitimate interest in knowing who our clients or customers are, so that we can contact them if necessary. We also need to know who is using our services and whether they are being used in accordance with our terms of use; that is, Article 6(1)(f) of the GDPR (legitimate interests) applies in this matter.
Note: Users should check the following sections (as required):
Registration Using Real Names
Since our business operations require us to know who our clients or customers are, registration is only possible using your real name (full name) and not a pseudonym.
Registration using pseudonyms
You can use a pseudonym when registering, which means you do not have to register with your real name. This ensures that we cannot process your real name.
Storage of the IP address
During registration, login, and account use, we store your IP address for security reasons so that we can verify legitimate use.
Public Profile
User profiles are publicly visible; that is, parts of the profiles can also be viewed on the Internet without having to enter a username and password.
Two-Factor Authentication (2FA)
Two-Factor Authentication (2FA) provides additional security when logging in, as it prevents you from logging in without a smartphone, for example. This technical measure to secure your account protects you against data loss or unauthorized access, even if your username and password were compromised. During the registration process, when logging in, or within the account itself, ycan find out which 2FA method is used.
Web hosting
| Web Hosting Overview 👥 Affected parties: visitors to the website 📓 Purpose: professional hosting of the website and operational security 🤝 Data processed: IP address, time of website visit, browser used, and other data. You can find more details below or on the respective web hosting provider’s website. 📅 Retention period: Depends on the respective provider, but is usually 2 weeks ⚖️ Legal basis: Art. 6(1)(f) GDPR (legitimate interests) |
What is web hosting?
Every time you visit a website these days, certain information—including personal data—is automatically generated and stored, including on this website. This data should be processed as sparingly as possible, and only for valid reasons. By “website,” we mean all websites on your domain, i.e., everything from the homepage to the very last subpage (like this one here). By “domain,” we mean example.uk or examplepage.com.
When you want to view a website on a screen, you use a program called a web browser. You probably know the names of some web browsers: Google Chrome, Microsoft Edge, Mozilla Firefox, and Apple Safari.
The web browser must connect to another computer that stores the website's code: the web server. Operating a web server is complicated and time-consuming, which is why this task is usually handled by professional providers. They offer web hosting and thus ensure the reliable and seamless storage of website data.
Whenever the browser on your computer establishes a connection (desktop, laptop, smartphone) and whenever data is transferred to and from the web server, personal data may be processed. After all, your computer stores data, and the web server must also retain the data for a certain period of time to ensure it can function properly.
Illustration:
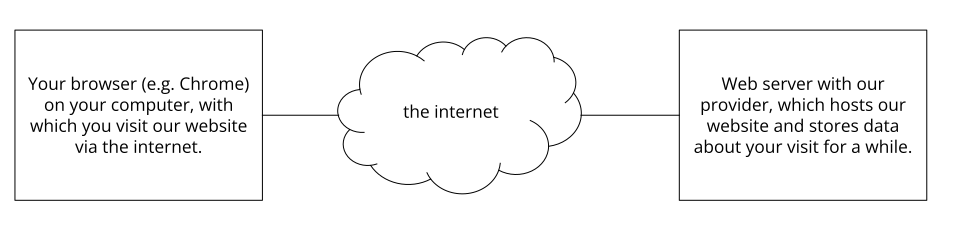
Why do we process personal data?
The purposes of data processing are:
- Professional website hosting and operational security
- To maintain both operational and IT security
- Anonymous analysis of access patterns to improve our services and, if necessary, for legal action or the pursuit of claims.li>
What data is processed?
Even while you are visiting our website, our web server—that is, the computer on which this website is hosted—usually automatically collects data such as
- the full address (URL) of the website visited (e.g., https://www.examplepage.uk/examplesubpage.html?tid=122077330)
- browser and browser version (e.g., Chrome 87)
- the operating system used (e.g., Windows 10)
- the address (URL) of the previously visited page (referrer URL) (e.g., https://www.examplepage.uk/icamefromhere.html/)
- the host name and IP address of the device from which the website is being accessed (e.g., COMPUTERNAME and 194.23.43.121)
- date and time
- in so-called web server log files
How long is the data stored?
Generally, the data mentioned above are stored for two weeks and are then automatically deleted. We do not share this data with third parties, but we cannot rule out the possibility that this data may be accessed by the authorities in the event of illegal conduct.
In short: Your visit is logged by our provider (the company that hosts our website on special computers (servers)), but we do not share your data without your consent!
Legal basis
The lawfulness of processing personal data in the context of web hosting is based on Article 6(1)(f) of the GDPR (protection of legitimate interests), as the use of professional hosting services provided by a third-party provider is necessary to present the company in a secure and user-friendly manner on the Internet, as well as to be able to track any attacks and claims, if necessary.
Hetzner Privacy Policy
We use Hetzner for our website; among other things, Hetzner is a web hosting provider. The provider of this service is the German company Hetzner Online GmbH, located at Industriestr. 25, 91710 Gunzenhausen, Germany. You can find out more about the data processed through the use of Hetzner in their Privacy Policy at https://www.hetzner.com/de/rechtliches/datenschutz.
Hetzner Data Processing Agreement (DPA)
In accordance with Article 28 of the General Data Protection Regulation (GDPR), we have entered into a Data Processing Agreement (DPA) with Hetzner. You can read about what exactly a DPA is—and, in particular, what must be included in a DPA—in our general section titled “Data Processing Agreement (DPA).”
This contract is required by law because Hetzner processes personal data on our behalf. It specifies that Hetzner may only process the data it receives from us in accordance with our instructions and must comply with the GDPR. You can find the link to the Data Processing Agreement (DPA) at https://docs.hetzner.com/de/general/general-terms-and-conditions/data-privacy-faq/.
Web Analytics
| Web Analytics Privacy Policy Overview 👥 Affected parties: visitors to the website 🤝 Purpose: Analysis of visitor information to optimize the website. 📓 Processed data: Access statistics containing data such as location of access, device data, duration and time of access, navigation behavior, click behavior, and IP addresses. You can find more details on this directly from the respective web analytics tool. 📅 Retention period: depending on the respective web analytics tool used ⚖️ Legal basis: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What Is Web Analytics?
We use software on our website—known as web analytics—to evaluate visitor behavior. This software collects data, which the analytics tool provider (also known as a tracking tool) stores, manages, and processes. This data is used to generate analyses of user behavior on our website, which we, as the website operator, receive. Most tools also offer various testing options. These allow us, for example, to test which offers or content our visitors prefer. To do this, we may show you two different offers for a limited period of time. After the test (a so-called A/B test), we know which product or content our website visitors find more interesting. For such testing, as well as for various other analyses, user profiles are created and the respective data is stored in cookies.
Why Do We Use Web Analytics?
We have a clear goal in mind when it comes to our website: we want to offer the best website in our industry. Therefore, we want to provide you with both the best and most interesting offerings, as well as a comfortable experience when you visit our website. Using web analytics tools, we can track the behavior of our website visitors and then improve our website accordingly—for your benefit and ours. For example, we can see the average age of our visitors, where they come from, the times when our website receives the most traffic, and which content or products are particularly popular. All this information helps us optimize our website and tailor it to your needs, interests, and preferences.
What data is processed?
The specific data that is stored depends on the analytics tools being used. However, in general, data such as the content you view on our website is stored, as well as, for example, which buttons or links you click, when you open a page, which browser you use, which device (PC, tablet, smartphone, etc.) you use to visit the website, or which computer system you use. If you have consented to the collection of location data, this data may also be processed by the provider of the web analytics tool.
Furthermore, your IP address is also stored. According to the General Data Protection Regulation (GDPR), IP addresses constitute personal data. However, your IP address is usually stored in a pseudonymized form (i.e., in an unrecognizable and abbreviated form). No directly linkable data—such as your name, age, address, or email address—is stored for testing purposes, web analytics, or website optimization. If such data is collected, it is retained in a pseudonymized form. Therefore, it cannot be used to identify you personally.
The following example demonstrates Google Analytics' functionality as an example of client-side web tracking using JavaScript code.

The storage period for each type of data always depends on the provider. Some cookies retain data for only a few minutes or until you leave the website, while others can store data for several years.
Duration of Data Processing
If we have any further information regarding the duration of data processing, you will find it below. We generally process personal data only for as long as is absolutely necessary to provide products and services. The retention period may be extended if required by law, such as for accounting purposes.
Right to Object
You also have the option and the right to revoke your consent to the use of cookies or third-party providers at any time. You can do this either through our cookie management tool or through other opt-out features. For example, you can also prevent data processing by cookies by managing, disabling, or deleting cookies in your browser.
Legal basis
The use of web analytics requires your consent, which we obtained through our cookie pop-up. Pursuant to Article 6(1)(a) of the GDPR (consent), this consent serves as the legal basis for the processing of personal data, such as data collected through web analytics tools.
In addition to consent, we have a legitimate interest in analyzing the behavior of website visitors, which enables us to improve our offerings both technically and economically. Web analytics allows us to detect website errors, identify attacks, and improve profitability. The legal basis for this is Article 6(1)(f) of the GDPR (legitimate interests). However, we only use these tools if you have given your consent.
Since web analytics tools use cookies, we recommend that you read our privacy policy regarding cookies. If you want to find out which of your data are stored and processed, you should read the privacy policies of the respective tools.
If available, information on special web analytics tools can be found in the following sections.
Facebook Pixel Privacy Policy
We use Facebook’s Facebook Pixel on our website. To do so, we have implemented a code snippet on our website. The Facebook Pixel is a segment of JavaScript code that, if you arrived at our website via Facebook ads, loads an array of functions that enable Facebook to track your user actions. For example, if you purchase a product on our website, the Facebook Pixel is triggered and stores your actions on our website in one or more cookies. These cookies allow Facebook to link your user data (customer data such as IP address and user ID) to the data in your Facebook account. Afterward, Facebook deletes your data. The collected data is anonymous and inaccessible and can only be used for advertising purposes. If you are a Facebook user and are logged in, your visit to our website is automatically associated with your Facebook account.
We want to show our products or services exclusively to people who are interested in them. With the help of the Facebook pixel, we can better tailor our advertising to your preferences and interests. As a result, Facebook users see relevant ads (if they have enabled personalized ads). In addition, Facebook uses the collected data for analytical purposes and for its own advertising.
Below, we will show you the cookies that were set on a test page with the Facebook pixel integrated into it. Please note that these cookies are only examples. Depending on the interactions that take place on our website, different cookies are set.
Name: _fbp
Value: fb.1.1568287647279.257405483-6122077330-7
Purpose: Facebook uses this cookie to display advertising products.
Expiration date: after 3 months
Name: fr
Value: 0aPf312HOS5Pboo2r..Bdeiuf…1.0.Bdeiuf.
Purpose: This cookie is used to ensure that Facebook pixels function properly.
Expiration date: after 3 months
Name: comment_author_50ae8267e2bdf1253ec1a5769f48e062122077330-3
Value: Name of the author
Purpose: This cookie stores the text and name of a user who, for example, leaves a comment.
Expiration date: after 12 months
Name: comment_author_url_50ae8267e2bdf1253ec1a5769f48e062
Value: https%3A%2F%2Fwww.testseite…%2F (URL of the author)
Purpose: This cookie stores the URL of the website that the user enters into a text box on our website.
Expiration date: after 12 months
Name: comment_author_email_50ae8267e2bdf1253ec1a5769f48e062
Value: the author's email address
Purpose: This cookie stores the user's email address if they provided it on the website.
Expiration date: after 12 months
Note: The cookies mentioned above relate to an individual user's behavior. Furthermore, especially with regard to the use of cookies, changes at Facebook can never be ruled out.
If you have a Facebook account, you can change your ad settings yourself at https://www.facebook.com/ads/preferences/?entry_product=ad_settings_screen. If you are not a Facebook user, you can manage your user-based online advertising at https://www.youronlinechoices.com/uk/your-ad-choices. There, you can choose to enable or disable any providers.
Facebook processes your data, among other things, in the United States. Facebook, or Meta Platforms, is an active participant in the EU-U.S. Data Privacy Framework, which governs the proper and secure transfer of personal data from EU citizens to the United States. For more information, visit https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Facebook uses what are known as Standard Contractual Clauses (Article 46(2) and (3) of the GDPR). Standard Contractual Clauses (SCCs) are template clauses provided by the European Commission and are designed to ensure that your data complies with European data protection standards, even when transferred to and stored in third countries (such as the United States). Through the EU-U.S. Data Privacy Framework and the Standard Contractual Clauses, Facebook commits to maintaining the European level of data protection when processing your relevant data, even if the data is stored, processed, and managed in the U.S. These clauses are based on an implementing decision by the European Commission. You can find the decision and the corresponding Standard Contractual Clauses here: https://ec.europa.eu/commission/presscorner/detail/en/ip_21_2847.
The Facebook Data Processing Terms, which refer to the Standard Contractual Clauses, can be found at https://www.facebook.com/legal/terms/dataprocessing.
If you would like to learn more about Facebook's data protection, we recommend that you review the company's internal data policies at https://www.facebook.com/policy.php.
Matomo Privacy Policy
We use Matomo, a web analytics tool, on our website. The provider of this service is InnoCraft Ltd, 7 Waterloo Quay PO625, 6140 Wellington, New Zealand. You can find out more about the data processed when using Matomo in their Privacy Policy at https://matomo.org/privacy-policy/. Questions regarding data protection can be sent by email to privacy@matomo.org.
Matomo On-Premise Privacy Policy
We use the privacy-friendly analytics program Matomo On-Premise on our website. With the on-premise version, Matomo is installed on our own server. This means that we act as the operator of the software, and any data we may collect from you is stored directly by us. Data processing therefore remains entirely under our control. The service provider is the New Zealand company InnoCraft Ltd, 7 Waterloo Quay PO625, 6140 Wellington, New Zealand.
If you would like to learn more about how Matomo On-Premise processes data, you can also contact us. In addition, we recommend reading Matomo’s privacy policy at https://matomo.org/privacy-policy/.
Matomo On-Premise (without cookies)
It is common practice for many web analytics tools to collect and process a large amount of personal data for analysis purposes and for their own marketing using so-called cookies. Cookies are small text files that are usually stored in your browser and may contain personal data. We want to respect and protect your privacy as much as possible. That’s why we decided to take a different approach and use Matomo On-Premise entirely without cookies. While we can use Matomo to perform various measurements and web analytics, it does not store any of your personal data in cookies. Matomo On-Premise without cookies is one of the most privacy-friendly web analytics services on the market.
Email Marketing
| Email Marketing Overview 👥 Affected parties: newsletter subscribers 🤝 Purpose: direct marketing via email, notification of events relevant to the system 📓 Processed data: data entered during registration, but at least the email address. You can find more details on this in the respective email marketing tool used. 📅 Storage duration: for the duration of the subscription ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What Is Email Marketing?
We use email marketing to keep you informed. If you have agreed to receive our emails or newsletters, your data will be processed and stored. Email marketing is a form of online marketing. In this type of marketing, news or general information about a company, product, or service is emailed to a specific group of people who are interested in it.
If you want to participate in our email marketing (usually via newsletter), you generally just need to register with your email address. To do this, you must fill out and submit an online form. However, we may also ask for your title and name so that we can address you personally in our emails.
Newsletter registration generally uses the so-called “double opt-in procedure.” After you sign up for our newsletter on our website, you will receive an email through which you can confirm your subscription. This ensures that you are the owner of the email address you used to sign up and prevents anyone from signing up with a third-party email address. We, or a notification tool we use, will log every single registration. This is necessary so that we can ensure and prove that registration processes are carried out legally and correctly. In general, the time of registration and registration confirmation are stored, along with your IP address. Furthermore, any changes you make to the data we have on file are also logged.
Why Do We Use Email Marketing?
Of course, we want to stay in touch with you and keep you informed about the most important news regarding our company. To that end, we use email marketing—often simply referred to as “newsletters”—as an essential part of our online marketing. If you consent to this or if it is permitted by law, we will send you newsletters, system emails, or other notifications via email. Whenever the term “newsletter” is used in the following text, it primarily refers to emails sent on a regular basis. We certainly do not want to bother you with our newsletter in any way. Therefore, we genuinely strive to provide only relevant and interesting content. In our emails, you can, for example, learn more about our company and our services or products. Since we are continuously improving our offerings, our newsletter will always provide you with the latest news or special, lucrative promotions. Should we engage a service provider for our email marketing who offers a professional mailing tool, we do so in order to provide you with fast and secure newsletters. The purpose of our email marketing is to inform you about new offers and to help us achieve our business goals.
What data is processed?
If you subscribe to our newsletter through our website, you will then need to confirm your subscription to our email list via an email that we will send you. In addition to your IP address and email address, your name, address, and phone number may also be stored. However, this will only occur if you consent to the retention of this data. Any data marked as such is necessary for you to use the service we offer. Providing this information is voluntary, but failure to do so will prevent you from using this service. Furthermore, information about your device or the type of content you prefer on our website may also be stored. In the section “Automatic Data Storage,” you can learn more about how your data is stored when you visit a website. We record your informed consent so that we can always demonstrate compliance with applicable laws.
Duration of Data Processing
If you unsubscribe from our email/newsletter distribution list, we may store your email address for up to three years based on our legitimate interests, so that we can retain proof of your consent at that time. We are only permitted to process this data if we need to defend ourselves against any claims.
However, if you confirm that you have given us your consent to subscribe to the newsletter, you may submit an individual request for erasure at any time. Furthermore, if you permanently withdraw your consent, we reserve the right to add your email address to a blacklist. But as long as you have voluntarily subscribed to our newsletter, we will, of course, keep your email address on file.
Cancellation – How can I cancel my subscription?
You can cancel your newsletter subscription at any time. All you have to do is withdraw your consent to receive the newsletter. This usually takes just a few seconds or a few clicks. Most of the time, you’ll find a link at the end of every email that allows you to cancel your subscription. If you can’t find the link in the newsletter, you can contact us by email, and we’ll cancel your newsletter subscription for you right away.
Legal basis
Our newsletter is sent based on your consent ( Article 6 (1) (a) of the GDPR). This means that we are only permitted to send you a newsletter if you have actively subscribed to it in advance. Furthermore, we may also send you advertising messages pursuant to Section 7(3) of the UWG (Unfair Competition Act), provided that you have become our customer and have not objected to the use of your email address for direct marketing.
If available, you can find information about special email marketing services and how they process personal data in the following sections.
Klick-Tipp Privacy Policy
We use Klick-Tipp on our website, which is an email automation service. The service provider is the British company Klick-Tipp Limited, located at 15 Cambridge Court, 210 Shepherd’s Bush Road, London W67NJ, United Kingdom. You can find out more about the data processed through the use of Klick-Tipp in the privacy policy at https://www.klicktipp.com/datenschutzerklarung/.
Social Media
| Social Media Privacy Policy Overview 👥 Affected parties: website visitors 🤝 Purpose: Presenting and optimizing our services, staying in contact with visitors, interested parties, etc., as well as advertising 📓 Processed data: Data such as phone numbers, email addresses, contact information, user behavior data, information about your device, and your IP address. You can find more details on this directly on the respective social media platform. 📅 Retention period: depending on the social media platforms used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What Is Social Media?
In addition to our website, we are also active on various social media platforms. In order for us to target interested users via social networks, user data may be processed. Additionally, elements of social media platforms may be embedded directly into our website. This is the case, for example, when you click a so-called social button on our website and are redirected directly to our social media presence. So-called social media are websites and apps on which registered members can create and share content with other members, either publicly or within specific groups and networks.
Why Do We Use Social Media?
For years, social media platforms have been the place where people communicate and connect online. Through our social media presence, we can help interested people learn more about our products and services. The social media features integrated into our website allow you to access our social media content quickly and easily.
The data collected and processed when you use a social media channel is primarily used to conduct web analytics. The purpose of these analyses is to develop more precise and personalized marketing and advertising strategies. The data analyzed regarding your behavior on any social media platform can help draw appropriate conclusions about your interests. Furthermore, so-called user profiles can be created. As a result, the platforms may also present you with customized advertisements. To do this, cookies are typically placed in your browser to store data about your user behavior.
We generally assume that we will continue to be responsible under data protection law, even when using the services of a social media platform. However, the European Court of Justice has ruled that, within the meaning of Article 26 of the GDPR, in certain cases the operator of the social media platform may be jointly responsible with us. Should this be the case, we will point it out separately and operate on the basis of a related agreement. You will find the key terms of the agreement for the relevant platform below.
Please note that when you use social media platforms or our built-in features, your data may also be processed outside the European Union, as many social media channels—such as Facebook or Twitter—are U.S. companies. As a result, you may no longer be able to easily exercise or enforce your rights regarding your personal data.
What data is processed?
Exactly which data is stored and processed depends on the specific provider of the social media platform. However, it typically includes data such as phone numbers, email addresses, information you enter in contact forms, user data (such as which buttons you click, what you like, or who you follow), when you visited which pages, as well as information about your device and IP address. Most of this data is stored in cookies. If you have a profile on the social media platform you are visiting and are logged in, this data may be linked to your profile.
All data collected through social media platforms are also stored on the providers’ servers. This means that only the providers have access to the data and can provide you with the appropriate information or make changes on your behalf.
If you want to know exactly what data is stored and processed by social media providers and how you can object to the processing of that data, we recommend that you carefully read the privacy policy of the respective company. We also recommend that you contact the provider directly if you have any questions about data storage and processing or if you wish to exercise any related rights.
Duration of Data Processing
If we have any further information on this matter, we will provide details below regarding the duration of data processing. For example, the social media platform Facebook stores data until it is no longer needed for the company’s own purposes. However, customer data that is synchronized with your own user data is deleted within two days. Generally, we only process personal data for as long as is absolutely necessary to provide our services and products. However, this retention period may be extended if required by law, such as in the case of accounting.
Right to Object
You also retain the right and the option to revoke your consent to the use of cookies or third-party providers, such as embedded social media elements, at any time. You can do this either through our cookie management tool or through other opt-out features. For example, you can also prevent data collection via cookies by managing, disabling, or deleting cookies in your browser.
Since cookies may be used in conjunction with social media tools, we also recommend that you read our privacy policy regarding cookies. If you want to find out which of your data is stored and processed, we advise you to read the privacy policies of the respective tools.
Legal basis
If you have consented to the processing and storage of your data by integrated social media elements, this consent serves as the legal basis for data processing (Art. 6(1)(a) GDPR). Generally, provided you have given your consent, your data will also be stored and processed on the basis of our legitimate interest (Art. 6( 1(f) GDPR) in maintaining fast and effective communication with you and other customers and business partners. Nevertheless, we only use these tools if you have given your consent. Most social media platforms also set cookies on your browser to store data. We therefore recommend that you read our privacy policy regarding cookies carefully and review the privacy policy or cookie policy of the respective service provider.
In the following section, you can find information about specific social media platforms—provided that this information is available.
LinkedIn Privacy Policy
| LinkedIn Privacy Policy Overview 👥 Affected parties: website visitors 🤝 Purpose: optimization of our service 📓 Processed data: includes data on user behavior, information about your device, and IP address. More details can be found in the privacy policy below. 📅 Retention period: The data is generally deleted within 30 days ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is LinkedIn?
On our website, we use social plugins from the social media network LinkedIn, owned by LinkedIn Corporation, 2029 Stierlin Court, Mountain View, CA 94043, USA. Social plugins may include feeds, content sharing, or a link to our LinkedIn page. Social plugins are clearly marked with the well-known LinkedIn logo and, for example, allow you to share interesting content directly through our website. Furthermore, LinkedIn Ireland Unlimited Company, located at Wilton Place in Dublin, is responsible for data processing in the European Economic Area and Switzerland.
By embedding these plugins, data may be sent to, stored, and processed by LinkedIn. In this privacy policy, we want to inform you about what data is involved, how LinkedIn uses this data, and how you can manage or prevent the retention of your data.
LinkedIn is the largest social network for business contacts. Unlike Facebook, for example, LinkedIn focuses exclusively on building professional connections. As a result, companies can showcase their services and products on the platform and establish business relationships. Many people also use LinkedIn to find a job or to recruit suitable employees for their own companies. In Germany alone, the network has over 11 million members. In Austria, there are about 1.3 million.
Why do we use LinkedIn on our website?
We know how busy you are. You simply can’t keep up with every single social media channel. Even though it would really be worth it—as it is with our channels, since we’re constantly posting interesting news and articles worth sharing. That’s why we’ve added a feature to our website that lets you share interesting content directly on LinkedIn or link directly to our LinkedIn page. We view built-in social plugins as an additional service on our website. The data LinkedIn collects also helps us target potential advertising campaigns only to people who are interested in what we have to offer.
What data does LinkedIn store?
LinkedIn does not store any personal data simply because social plugins are integrated. LinkedIn refers to the data generated by plugins as “passive impressions.” However, if you click on a social plugin—for example, to share our content—the platform stores personal data as so-called “active impressions.” This occurs regardless of whether you have a LinkedIn account or not. If you are logged in, the collected data will be associated with your account.
When you interact with our plugins, your browser establishes a direct connection to LinkedIn’s servers. Through this connection, the company collects various usage data. This may include your IP address, login information, device information, or information about your internet or cellular service provider. If you use LinkedIn services on your smartphone, your location may also be identified (after you have given permission). Furthermore, LinkedIn may share this data with third-party advertisers in “hashed” form. Hashing means that a data set is converted into a string of characters. This encrypts the data, preventing individuals from being identified.
Most of the data regarding your user behavior is stored in cookies. These are small text files that are typically stored in your browser. In addition, LinkedIn may also use web beacons, pixel tags, display tags, and other device recognition technologies.
Various tests also show which cookies are set when a user interacts with a social plug-in. We do not claim that the information we found is exhaustive, as it is provided solely as an example. The following cookies were set without being logged in to LinkedIn:
Name: bcookie
Value: =2&34aab2aa-2ae1-4d2a-8baf-c2e2d7235c16122077330-
Purpose: Thiscookie is a so-called “browser ID cookie” and stores your identification number (ID).
Expiration date: after 2 years
Name: lang
Value: v=2&lang=en-gb
Purpose:This cookie saves your default or preferred language.
Expiration date: at the end of the session
Name: lidc
Value: 1818367:t=1571904767:s=AQF6KNnJ0G122077330…
Purpose:This cookie is used for routing. Routing tracks how you found your way to LinkedIn and how you navigate through the website.
Expiration date: after 24 hours
Name: rtc
Value: kt0lrv3NF3x3t6xvDgGrZGDKkX
Purpose:No further information could be found about this cookie.
Expiration date: after 2 minutes
Name: JSESSIONID
Value: ajax:1220773302900777718326218137
Purpose: This is a session cookie that LinkedIn uses to maintain anonymous user sessions on the server.
Expiration date: at the end of the session
Name: bscookie
Value: “v=1&201910230812…
Purpose: This cookie is a security cookie. LinkedIn describes it as a secure browser ID cookie.
Expiration date: after 2 years
Name: fid
Value: AQHj7Ii23ZBcqAAAA…
Purpose: We could not find any further information about this cookie.
Expiration date: after 7 days
Note: LinkedIn also works with third parties. That is why we identified the Google Analytics cookies _ga and _gat in our test.
How long and where is the data stored?
In general, LinkedIn retains your personal data for as long as the company deems it necessary to provide its services. However, LinkedIn deletes your personal data when you delete your account. In some exceptional cases, LinkedIn retains certain aggregated and anonymized data, even after an account is deleted. Once you delete your account, it may take up to one day before other people can no longer view your data. LinkedIn generally deletes the data within 30 days. However, LinkedIn retains data if it is necessary for legal reasons. Additionally, data that can no longer be linked to any specific person remains stored even after the account is closed. The data is stored on various servers in the United States and presumably also in Europe.
How can I delete my data or prevent it from being retained?
You have the right to access and delete your personal data at any time. In your LinkedIn account, you can manage, change, and delete your data. In addition, you can request a copy of your personal data from LinkedIn.
How to access account information in your LinkedIn profile:
On LinkedIn, click your profile icon and select the “Settings & Privacy” section. Now click “Privacy” and then the section titled “How LinkedIn uses your data.” Next, click “Change” in the row labeled “Manage your data and activity.” There, you can instantly view selected data about your web activity and your account history.
In your browser, you also have the option to prevent LinkedIn from processing your data. As mentioned above, LinkedIn stores most of its data using cookies that are placed in your browser. You can manage, disable, or delete these cookies. Depending on which browser you use, these settings work slightly differently. You can find instructions for the most common browsers here:
Chrome: Clear, enable, and manage cookies in Chrome
Safari: Manage cookies and website data in Safari
Firefox: Clear cookies and site data in Firefox
Internet Explorer: Delete and manage cookies
Microsoft Edge: Delete cookies in Microsoft Edge
You can usually configure your browser to always notify you when a cookie is about to be set. Then you can decide on a case-by-case basis whether you want to allow the cookie or not.
Legal basis
If you have consented to the processing and storage of your data by integrated social media elements, your consent serves as the legal basis for data processing (Art. 6(1)(a) GDPR). Generally, your data is also stored and processed based on our legitimate interest (Art. 6(1)(f) GDPR) in maintaining fast and effective communication with you or other customers and business partners. We only use the integrated social media elements if you have given your consent. Most social media platforms also place cookies in your browser to store data. We therefore recommend that you read our privacy policy regarding cookies carefully and review the privacy policy or cookie policy of the respective service provider.
LinkedIn, therefore, processes data in the United States, among other countries. We would like to note that, according to the European Court of Justice, there is currently no adequate level of protection for data transfers to the United States. This can pose various risks to the legality and security of data processing.
LinkedIn uses standard contractual clauses approved by the EU Commission as the basis for data processing by recipients based in third countries (outside the European Union, Iceland, Liechtenstein, Norway, and especially in the U.S.) or for data transfers to those countries (= Art. 46, paragraphs 2 and 3 of the GDPR). These clauses require LinkedIn to comply with the EU’s data protection standards when processing relevant data outside the EU. These clauses are based on an implementing decision by the European Commission. You can find the decision and the clauses here: https://ec.europa.eu/commission/presscorner/detail/en/ip_21_2847
We have tried to provide you with the most important information about how LinkedIn processes data. Visit https://www.linkedin.com/legal/privacy-policy to learn more about how the social media network LinkedIn processes data.
Data Processing Agreement (DPA) LinkedIn
In accordance with Article 28 of the General Data Protection Regulation (GDPR), we have entered into a Data Processing Agreement (DPA) with LinkedIn. You can read about what exactly a DPA is—and, in particular, what must be included in a DPA—in our general section titled “Data Processing Agreement (DPA).”
This contract is required by law because LinkedIn processes personal data on our behalf. It clarifies that LinkedIn may only process data it receives from us in accordance with our instructions and must comply with the GDPR. You can find the link to the Data Processing Agreement (DPA) at https://www.linkedin.com/legal/l/dpa?.
Pinterest Privacy Policy
| Pinterest Privacy Policy Overview 👥 Affected parties: website visitors 🤝 Purpose: service optimization 📓 Processed data: data such as user behavior, device information, IP address, and search terms. You can find more details in the Privacy Policy below. 📅 Retention period: until Pinterest no longer needs the data for its purposes ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Pinterest?
On our website, we use buttons and widgets from the social media network Pinterest, operated by Pinterest Inc., 808 Brannan Street, San Francisco, CA 94103, USA. For the European region, the entity responsible for all aspects of privacy is the Irish company Pinterest Europe Ltd. (Palmerston House, 2nd Floor, Fenian Street, Dublin 2, Ireland).
Pinterest is a social network that specializes in visual content and photographs. Its name is a combination of the words “pin” and “interest.” Users can share ideas about various hobbies and interests on Pinterest and view profiles with photos—either publicly or within specific groups.
Why do we use Pinterest?
The social media platform Pinterest has been around for a few years now and remains one of the most visited and valued platforms. Pinterest is particularly well-suited to our industry because the platform is primarily known for its beautiful and interesting images. That is why we are, of course, also active on Pinterest and want to showcase our content in places other than our website. The data collected may also be used for advertising purposes, allowing us to show ads to precisely those people who are interested in our services or products.
What data does Pinterest process?
Pinterest may store so-called log data. This includes information about your browser, IP address, our website address, and your activities on it (e.g., when you click the "Save" or "Pin" button), along with your search history, the date and time of the request, and cookie and device data. If you interact with an embedded Pinterest feature, cookies that store various types of data may also be set in your browser. Most of the aforementioned log data, as well as preset language settings and clickstream data, are stored in cookies. Pinterest considers clickstream data to be information about your website behavior.
If you have a Pinterest account and are logged in, the data collected through our site may be linked to your account and used for advertising purposes. If you interact with our integrated Pinterest features, you will usually be redirected to the Pinterest page. Below is a sample list of cookies that may then be stored in your browser.
Name: _auth
Value: 0
Purpose: This cookie is used for authentication. For example, a value such as your “username” can be stored in it.
Expiration date: after one year
Name: _pinterest_referrer
Value: 1
Purpose: This cookie stores information indicating that you came to Pinterest via our website. Thus, the URL of our website is retained.
Expiration date: after the session ends
Name: _pinterest_sess
Value: … 9HRHZvVE0rQlUxdG89
Purpose: This cookie is used to log in to Pinterest and contains user IDs, authentication tokens, and timestamps.
Expiration date: after one year
Name: _routing_id
Value: “8d850ddd-4fb8-499c-961c-77efae9d4065 122077330 -8”
Purpose: This cookie contains an assigned value that is used to identify a specific routing destination.
Expiration date: after one day
Name: cm_sub
Value: denied
Purpose: This cookie stores user IDs and timestamps.
Expiration date: after one year
Name: csrftoken
Value: 9e49145c82a93d34fd933b0fd8446165 122077330-1
Purpose: This cookie is most certainly set for security reasons to prevent fraudulent requests. However, we were unable to find more specific information.
Expiration date: after one year
Name: sessionFunnelEventLogged
Value: 1
Purpose: We have not yet been able to find more information about this cookie.
Expiration date: after one day
How long and where is the data retained?
Pinterest basically stores the collected data until it is no longer needed for the company’s purposes. As soon as storing this data is no longer necessary—for example, to comply with legal regulations—the data is either deleted or anonymized so that you can no longer be identified as an individual. The data may also be stored on servers in the United States.
Right to Object
You also have the right and the option to revoke your consent to the use of cookies or third-party providers such as Pinterest at any time. You can do this either through our cookie management tool or through other opt-out features. For example, you can also prevent cookies from storing data by managing, disabling, or deleting cookies in your browser.
Since cookies can be used with embedded Pinterest elements, we also recommend that you read our general privacy policy regarding cookies. To find out which of your data are stored and processed, you should read the privacy policies of the respective tools.
Legal basis
If you have consented to the processing and storage of your data by integrated social media elements, this consent serves as the legal basis for data processing (Art. 6(1)(a) GDPR). Generally, your data is also stored and processed based on our legitimate interest (Art. 6(1)(f) GDPR) in maintaining fast and effective communication with you or other customers and business partners. Nevertheless, we only use the tool if you have given your consent to do so. Most social media platforms also place cookies in your browser to store data. We therefore recommend that you read our privacy policy regarding cookies carefully and review the privacy policy or cookie policy of the respective service provider.
Pinterest processes data in the United States, among other countries. We would like to note that, according to the European Court of Justice, there is currently no adequate level of protection for data transfers to the United States. This can pose various risks to the legality and security of data processing.
Pinterest uses standard contractual clauses approved by the European Commission as the basis for data processing by recipients based in third countries (outside the European Union, Iceland, Liechtenstein, Norway, and especially the United States) or for data transfers to those countries (= Article 46, paragraphs 2 and 3 of the GDPR). These clauses require Pinterest to comply with the EU’s data protection standards when processing relevant data outside the EU. These clauses are based on an implementing decision by the European Commission. You can find the decision and the clauses here: https://ec.europa.eu/commission/presscorner/detail/en/ip_21_2847
We hope we have provided you with the most important information about how Pinterest processes data. You can learn more about Pinterest’s privacy guidelines at https://policy.pinterest.com/en-gb/privacy-policy.
Twitter Privacy Policy
| Twitter Privacy Policy Overview 👥 Affected parties: website visitors 🤝 Purpose: optimizing our service 📓 Processed data: includes data on user behavior, information about your device, and your IP address. More details can be found in the privacy policy below. 📅 Retention period: Twitter deletes data collected from other websites after a maximum of 30 days ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Twitter?
We have integrated Twitter features into our website. These include, for example, embedded tweets, timelines, buttons, and hashtags. Twitter is a short-message service and social media platform operated by Twitter Inc., One Cumberland Place, Fenian Street, Dublin 2 D02 AX07, Ireland.
To the best of our knowledge, within the European Economic Area and Switzerland, simply integrating the Twitter feature does not result in the transfer of any personal data or data about your web activities to Twitter. Only when you interact with the Twitter features—such as by clicking a button—might data be sent to Twitter, where it is stored and processed. We have no control over this data processing and assume no responsibility for it. In this privacy statement, we aim to provide you with an overview of what data Twitter stores, how Twitter uses this data, and how you can largely protect yourself from data transmission.
For some, Twitter is a news service; for others, a social media platform; and for still others, a microblogging service. All of these terms are valid and mean pretty much the same thing.
Both individuals and companies use Twitter to communicate with interested people via short messages. Twitter limits each message to 280 characters. These messages are called “tweets.” Unlike Facebook, for example, the service does not focus on expanding a network of “friends,” but rather aims to be seen as an open, global news platform. On Twitter, you can also have an anonymous account, and tweets can be deleted by either the company or the users themselves.
Why do we use Twitter on our website?
Like many other websites and companies, we try to use different channels to offer our services and communicate with our customers. Twitter is a truly useful “micro” news service, which is why it has become so dear to us. We regularly tweet or retweet exciting, funny, or interesting content. We understand that you don’t have time to follow every single channel, as you surely have plenty of other things to do. That’s why we’ve also integrated Twitter features into our website. This way, you can follow our Twitter activity “right here on the site” or visit our Twitter page via a direct link. With this integration, we aim to enhance the service and user-friendliness of our website.
What data does Twitter store?
You will find integrated Twitter features on some of our subpages. If you interact with Twitter content—for example, by clicking a button—Twitter may collect and store data. This can happen even if you do not have a Twitter account yourself. Twitter refers to this data as “log data.” It includes demographic data, browser cookie IDs, your smartphone’s ID, hashed email addresses, and information about which pages you have visited on Twitter and what actions you have taken there. Of course, Twitter stores more data if you have a Twitter account and are logged in. This data is typically stored using cookies. Cookies are small text files that are usually stored in your browser and transmit various information to Twitter.
We will now show you which cookies are set if you are not logged in to Twitter but visit a website with built-in Twitter features. Please consider this list as an example. We do not claim that this list is exhaustive, since the set of cookies is constantly changing and depends on your individual interactions with Twitter content.
The following cookies were used in our test:
Name: personalization_id
Value: “v1_cSJIsogU51SeE122077330”
Purpose: This cookie stores information about how you use the website and which ad may have led you to Twitter.
Expiration date: after 2 years
Name: lang
Value: en
Purpose: This cookie stores your default or preferred language.
Expiration date: at the end of the session
Name: guest_id
Value: 122077330v1%3A157132626
Purpose: This cookie is set to identify you as a guest.
Expiration date: after 2 years
Name: fm
Value: 0
Purpose: Unfortunately , we were unable to determine the purpose of this cookie.
Expiration date: at the end of the session
Name: external_referer
Value: 1220773302beTA0sf5lkMrlGt
Purpose: This cookie collects anonymous data, such as how often you visit Twitter and how long you stay on Twitter.
Expiration date: after 6 days
Name: eu_cn
Value: 1
Purpose: This cookie stores user activity and is used for Twitter’s various advertising purposes.
Expiration date: after one year
Name: ct0
Value: c1179f07163a365d2ed7aad84c99d966
Purpose: Unfortunately , we could not find any information about this cookie.
Expiration date: after 6 hours
Name: _twitter_sess
Value: 53D%253D–dd0248122077330-
Purpose: This cookieallows youto use features on Twitter’s website.
Expiration date: at the end of the session
Note: Twitteralso works with third parties. Therefore, we identified the three Google Analytics cookies—_ga, _gat, and _gid—in our test.
On the one hand, Twitter uses the collected data to gain a better understanding of user behavior and, as a result, to improve its own services and advertising offerings. On the other hand, the data is also used for internal security measures.
How long and where is the data stored?
When Twitter collects data from other websites, after a maximum of 30 days, that data will be deleted, summarized, or otherwise obscured. Twitter’s servers are located in various data centers in the United States. Accordingly, it can be assumed that the collected data will be gathered and stored in the United States. In our research, we were unable to clearly determine whether Twitter also owns servers in Europe. Generally, Twitter may retain collected data until the data is no longer useful to the company, until you delete the data, or until a potential statutory retention period has expired.
How can I delete my data or prevent it from being retained?
In its Privacy Policy, Twitter repeatedly emphasizes that it does not store data from visits to external websites, provided that you or your browser are located in the European Economic Area or Switzerland. However, if you interact directly with Twitter, the company will, of course, store your data.
If you have a Twitter account, you can manage your data by clicking “More” under the “Profile” button. Then click “Settings and privacy.” Here you can manage data processing on a case-by-case basis.
If you don't have a Twitter account, you can go to twitter.com and click “Settings.” Under “Personalization and data,” you can manage the data collected about you.
As mentioned above, most data is stored using cookies, which you can manage, disable, or delete in your browser. Please note that when you change your cookie settings in your browser, those changes will only apply to that specific browser. This means that if you use a different browser in the future, you will need to manage your cookie settings there again. Below, you will find instructions for managing cookies in the most popular browsers.
Chrome: Clear, enable, and manage cookies in Chrome
Safari: Manage cookies and website data in Safari
Firefox: Clear cookies and site data in Firefox
Internet Explorer: Delete and manage cookies
Microsoft Edge: Delete cookies in Microsoft Edge
You can also set your browser to notify you about each individual cookie. This allows you to decide on a case-by-case basis whether to accept or reject a cookie.
Twitter also uses the data for personalized advertising both on and off Twitter. You can turn off personalized advertising in the settings under “Personalization and data.” If you use Twitter in a browser, you can disable personalized advertising at http://optout.aboutads.info/?c=2&lang=EN.
Legal basis
If you have consented to the processing and storage of your data by integrated social media elements, this consent serves as the legal basis for data processing (Art. 6(1)(a) GDPR). Generally, your data is also stored and processed based on our legitimate interest (Art. 6(1)(f) GDPR) in maintaining fast and effective communication with you or other customers and business partners. We only use integrated social media elements if you have given your consent. Most social media platforms also place cookies in your browser to store data. We therefore recommend that you read our privacy policy regarding cookies carefully and also review the privacy policy or cookie policy of the respective service provider.
Twitter processes data in the United States, among other countries. We would like to note that, according to the European Court of Justice, there is currently no adequate level of protection for data transfers to the United States. This can pose various risks to the legality and security of data processing.
Twitter uses standard contractual clauses, which are approved by the European Commission, as the basis for data processing by recipients based in third countries (outside the European Union, Iceland, Liechtenstein, Norway, and especially the United States) or for data transfers to those countries (= Art. 46, paragraphs 2 and 3 of the GDPR). These clauses require ShareThis to comply with the EU’s data protection standards when processing relevant data outside the EU. These clauses are based on an implementing decision by the European Commission. You can find the decision and the clauses here: https://ec.europa.eu/commission/presscorner/detail/en/ip_21_2847
We hope we have provided you with a basic overview of Twitter’s data processing. We do not receive any data from Twitter and are not responsible for how Twitter handles your data. If you have any further questions on this topic, we recommend that you read Twitter’s privacy policy at https://twitter.com/en/privacy.
Cloud Services
| Cloud Services Privacy Policy Overview 👥 Affected parties: We, as the website operator, and you, as the website visitor 🤝 Purpose: security and data storage 📓 Processed data: Data such as your IP address, name, or technical data such as your browser version More details can be found below and in the individual privacy policies or in the privacy policies of the providers 📅 Duration of storage: In most cases, data is stored until it is no longer required to provide the service ⚖️ Legal bases: Article 6(1)(a) of the GDPR (consent), Article 6(1)(f) of the GDPR (legitimate interests) |
What are cloud services?
As a website operator, cloud services provide us with storage space and computing power via the Internet. Data can be transmitted to an external system, where it may be processed and stored via the Internet. The relevant cloud provider manages this data. Depending on specific requirements, an individual or a company can choose storage space or computing power. Cloud storage is accessed via an API or via storage protocols. API stands for Application Programming Interface, which is a programming interface that connects software with hardware components.
Why do we use cloud services?
We use cloud services for several reasons. A cloud service allows us to store our data securely. In addition, we can access the data from different locations and devices, which gives us greater flexibility and streamlines our work processes. Cloud storage also saves us money because we don’t have to set up and manage our own infrastructure for data storage and security. By storing our data centrally in the cloud, we can also expand our areas of application and manage our information much more effectively.
As a website operator or company, we use cloud services primarily for our own purposes. For example, we manage our calendar and store documents or other important information in the cloud. However, your personal data may also be stored. This can occur if you provide us with your contact information (e.g., name and email address) while we store our customer data with a cloud provider. Consequently, any of your data that we process may also be stored and processed on external servers. If we offer certain types of content via cloud services on our website, cookies may also be set for web analytics and advertising purposes. Furthermore, these cookies retain your settings (e.g., the language you use) so that you will be presented with your usual web environment the next time you visit our website.
What data is processed by cloud services?
Much of the data we store in the cloud cannot be used to identify you as an individual, but some data constitutes personal data as defined by the GDPR. This often includes customer data such as name, address, IP address, or phone number, as well as technical device information. Videos, images, and audio files may also be stored in the cloud. Exactly how the data is collected and stored depends on the specific service. We strive to use only services that handle your data in a highly reliable and professional manner. Generally, services such as Amazon Drive have access to the stored files in order to provide their services accordingly. However, these services require your consent for certain purposes (such as the right to copy files for security reasons). The data will be processed and handled as part of the services provided and in compliance with applicable laws. This also includes compliance with the GDPR for U.S. providers (via the standard contractual clauses). In some cases, cloud services also collaborate with third parties who may process data under instructions and in accordance with privacy policies and other security measures. At this point, we would like to emphasize again that all well-known cloud services (such as Amazon Drive, Google Drive, or Microsoft OneDrive) obtain the right to access stored content in order to offer and optimize their own services accordingly.
Duration of Data Processing
We will provide information below regarding the duration of data processing, provided we have further details on this matter. In general, cloud services store data until you or we revoke the data storage or delete the retained data. In general, personal data is stored only for as long as necessary to provide the respective services. However, it may take up to several months to delete your data from the cloud. This may occur because data is usually not stored on just one server but distributed across multiple servers.
Right to Object
You also have the right and the option to revoke your consent to data storage in the cloud at any time. If cookies are used, you also have the right to withdraw your consent. You can do this either through our cookie management tool or through other opt-out features. For example, you can also prevent data collection via cookies by managing, disabling, or deleting the cookies in your browser. We also recommend that you read our general privacy policy regarding cookies. To find out exactly which of your data is stored and processed, you should read the privacy policy of the respective cloud provider.
Legal Basis
We use cloud services primarily based on our legitimate interests (Art. 6, para. 1, lit. f of the GDPR) in having robust security and storage systems.
Certain types of processing, in particular the use of cookies and storage functions, require your consent. If you have consented to the processing and storage of your data by cloud services, this consent serves as the legal basis for data processing (Article 6(1)(a) of the GDPR). Most of the services we use place cookies in your browser to store data. Therefore, we recommend that you read our privacy policy regarding cookies carefully and review the privacy policy or cookie policy of the relevant service provider.
Information on special tools—if available—can be found in the following sections.
Dropbox Privacy Policy
We use Dropbox, an online storage service for files, photos, and videos, for our website. The service provider is the American company Dropbox Inc. The company’s European office is located in Ireland (One Park Place, 5th Floor, Upper Hatch Street, Dublin 2).
Dropbox also processes data in the United States, among other countries. We would like to note that, according to the European Court of Justice, there is currently no adequate level of protection for data transfers to the United States. This can pose various risks to the legality and security of data processing.
Dropbox uses standard contractual clauses approved by the European Commission as the basis for data processing by recipients based in third countries (i.e., outside the European Union, Iceland, Liechtenstein, and Norway—and thus especially in the United States) or for data transfers to those countries (= Article 46, paragraphs 2 and 3 of the GDPR). Standard Contractual Clauses (SCCs) are legal templates provided by the European Commission. Their purpose is to ensure that your data complies with European data protection standards, even if your data is transferred to and stored in third countries (such as the United States). Through these clauses, Dropbox commits to complying with the EU’s level of data protection when processing relevant data, even if it is stored, processed, and managed in the United States. These clauses are based on an implementing decision by the European Commission. You can find the decision and the standard contractual clauses here: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=en
The Data Processing Agreement, which corresponds to the Standard Contractual Clauses, can be found at https://assets.dropbox.com/documents/en/legal/dfb-data-processing-agreement.pdf.
You can find out more about the data processed when using Dropbox in the Privacy Policy at https://www.dropbox.com/privacy.
Introduction to Online Map Services
| Online Map Services Privacy Policy Overview 👥 Affected parties: website visitors 🤝 Purpose: Improvement of user experience 📓 Processed data: The data processed depends heavily on the services used. Typically, this includes your IP address, location data, search queries, and/or technical data. You can find more details on this under the respective tools used. 📅 Storage duration: depends on the tools used ⚖️ Legal bases: Article 6(1)(a) of the GDPR (consent), Article 6(1)(f) of the GDPR (legitimate interests) |
What Are Online Map Services?
We also use online map services on our website as an additional feature. Google Maps is probably the service you’re most familiar with. But there are also other providers that specialize in creating digital maps. These services allow us to display locations, route maps, or other geographic information directly on our website. Thanks to an integrated map service, you no longer have to leave our website to, for example, view the route to a location. To ensure that the online map functions properly on our website, we have embedded map elements within our HTML code. This enables the services to display street maps, the Earth’s surface, or aerial and satellite imagery. If you use the embedded map service, your data will be transmitted to the service provider, where it will be stored. This may also include your personal data.
Why do we use online map services on our website?
Generally speaking, it is essential for us to ensure you have a pleasant experience on our website. Of course, we know that you’ll most likely only enjoy your time here if you can easily navigate the site and find all the information you need quickly and easily. Therefore, we decided that an online map system could significantly improve our website’s service. After all, you can use the map system to easily view route descriptions, locations, or any other points of interest—without leaving our site. Needless to say, it’s also very convenient that you can easily see where our company headquarters are located so that you can find us quickly and safely. As you can see, there are many advantages—and we clearly consider online map services on our website to be an integral part of our customer service.
What data do online map services store?
If you open a page on our website that includes an online map feature, your personal data may be transmitted to the relevant service, where it may be stored. This usually includes your IP address, which may also be used to determine your approximate location. In addition to your IP address, data such as the search terms you entered, as well as your longitude and latitude coordinates, will be stored. If, for example, you enter an address for route planning, this data will also be stored. This data is not stored by us but rather on the servers of the integrated tools. You can think of it this way: You may be on our website, but when you interact with a mapping service, that interaction is actually taking place on their website. Furthermore, to ensure the service functions properly, at least one cookie is usually set in your browser. For example, Google Maps also uses cookies to track user behavior, which it uses to optimize its own service and deliver personalized advertising. You can learn more about cookies in our “Cookies” section.
How long is the data stored, and where is it stored?
Every online map service processes different types of user data. If we have additional information, we will provide details about the duration of data processing in the corresponding sections for each tool below. Generally, personal data is retained only for as long as necessary to provide the service. Google Maps, for example, stores certain data for a specified period of time, but you must delete other data yourself. At Mapbox, for example, your IP address is stored for 30 days, after which it is deleted. As you can see, each tool stores data for different lengths of time. We therefore recommend that you take a closer look at the privacy policies of the tools used.
The providers may use cookies to store data about your user behavior in connection with their map services. You can find more information about cookies in our “Cookies” section, but you can most likely also find out which cookies may be used in the individual providers’ privacy policies. In most cases, however, this is only a sample list and is not exhaustive.
Right to Object
You always have the option and the right to access your personal data and to object to its use and processing. You can also revoke the consent you gave us at any time. This is usually easiest to do through the cookie consent tool. However, there are other opt-out tools you can use. You can also manage, delete, or disable any cookies set by the providers we use yourself with just a few mouse clicks. However, this may cause some service features to stop working as usual. How you manage cookies also depends on your browser. In our “Cookies” section, you’ll find links to instructions for the most popular browsers.
Legal Basis
If you have consented to the use of an online map service, the legal basis for the corresponding data processing is this consent. According to Article 6, Paragraph 1, subparagraph (consent), this consent serves as the legal basis for the processing of personal data that may be collected by an online map service.
We also have a legitimate interest in using an online map service to optimize the service we provide on our website. The corresponding legal basis for this is Article 6(1)(f) of the GDPR (legitimate interests). However, we only use an online map service if you have given your consent. We definitely wanted to emphasize this point once again.
You can find information on specific online map services—if available—in the following sections.
Miscellaneous Overview
| Miscellaneous Privacy Policy Overview 👥 Affected parties: website visitors 🤝 Purpose: Improvement of user experience 📓 Processed data: The data processed depends heavily on the services used. Usually, it includes an IP address and/or technical data. You can find more details on this in the sections for the respective tools. 📅 Storage duration: depends on the tools used ⚖️ Legal bases: Article 6(1)(a) of the GDPR (consent), Article 6(1)(f) of the GDPR (legitimate interests) |
What is included in “Miscellaneous”?
The “Miscellaneous” category includes any services that do not fall into any of the above categories. These are typically various plugins and integrated elements designed to enhance our website. Generally, these functions are obtained from third parties and integrated into our website. They may include, for example, web search services such as Algolia Place, Giphy, and Programmable Search Engine, or online services for weather data such as OpenWeather.
Why do we use these third parties?
Through our website, we aim to provide you with the best online experience in our industry. Websites have long been much more than just a business card for companies. Instead, they are a space designed to help you find what you’re looking for. And to make our website even more interesting and helpful for you, we use various third-party services.
What data is processed?
Whenever elements are integrated into our website, your IP address will be transmitted to the respective provider, where it will be stored and processed. This is necessary to send the content to your browser, which will then display it for you. In addition, service providers may also use pixel tags or web beacons. These are small graphics on websites that can record a log file and generate analyses from it. Providers can use the information they receive in this way to improve their own marketing efforts. In addition to pixel tags, this information (e.g., which button you click or when you access which page) may also be stored in cookies. In addition to data analyses of your web behavior, technical information such as your browser type or operating system may also be stored there. Some providers may also link the data they collect to other internal services or to third-party providers. Each provider handles your data differently. Therefore, we recommend that you carefully read the privacy policies of the respective services. We make every effort to use only services that handle data protection and privacy with the utmost care.
Duration of Data Processing
Below, we will provide you with information about the duration of data processing, provided we have further details on this matter. In general, we process personal data only for as long as is absolutely necessary to provide our services and products.
Legal Basis
If we ask for your consent and you agree to our use of a service, this consent serves as the legal basis for the processing of your data (Article 6(1)(a) of the GDPR). In addition to your consent, we have a legitimate interest in analyzing the behavior of our website visitors in order to improve our offerings both technically and economically. The legal basis for this is Article 6(1)(f) of the GDPR (legitimate interests). However, we only use such tools if you have given your consent.
Information on special tools—if available—can be found in the following sections.
Weglot Privacy Policy
We use the Weglot translation service for our website. The service provider is the French company Weglot SAS, located at 7 Cité Paradis, 75010 Paris, France.
You can find out more about the data processed when using Weglot in the Privacy Policy at https://weglot.com/privacy/.
Explanation of the terminology used
We always strive to make our privacy policy as clear and understandable as possible. However, this is not always easy, especially when it comes to technical and legal matters. It is often advisable to use legal terms (such as “personal data”) or certain technical terms (such as “cookies” or “IP address”). But we don’t want to use such terms without providing an explanation. That is why you will find an alphabetical list of important terms used below. These are terms that we may not yet have explained sufficiently in the privacy policy. If we have adopted any of these terms from the GDPR—which are defined there—we will also include the relevant GDPR text here and add our own further explanations if necessary.
Processor
Definition pursuant to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“processor” means a natural or legal person, public authority, agency, or other body that processes personal data on behalf of the controller;
Explanation: As a company and a website owner, we are responsible for all your data that we process (i.e., the “controller”). In addition to the controller, there may also be so-called processors. This includes any company or person who processes personal data on our behalf. In addition to service providers such as tax consultants, processors can also be hosting or cloud providers, payment or newsletter providers, or large companies such as Google or Microsoft.
Consent
Definition pursuant to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“Consent”of the data subject means any freely given, specific, informed, and unambiguous indication of the data subject’s wishes by which he or she, through a statement or a clear affirmative action, signifies agreement to the processing of personal data relating to him or her;
Explanation: On websites, such consent is usually given through a cookie consent tool. You’ve most certainly come across these. Whenever you visit a website for the first time, you’ll usually be asked via a banner whether you agree to or consent to the processing of your data. You can usually also configure individual settings and thus decide for yourself what level of data processing you want to allow. If you do not give your consent, no personal data may be processed. Consent can, of course, also be given in writing—that is, not through a tool.
Personal Data
Definition pursuant to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“personal data” means any information relating to an identified or identifiable natural person (“data subject”); an identifiable natural person is one who can be identified, directly or indirectly, in particular by reference to an identifier such as a name, an identification number, location data, an online identifier, or to one or more factors specific to the physical, physiological, genetic, mental, economic, cultural, or social identity of that natural person;
Explanation: Personal data is any data that can identify you as an individual. This usually includes data such as:
- name
- address
- email address
- mailing address
- phone number
- birthday
- identification numbers such as Social Security number, tax identification number, ID card number, or student ID number
- banking data such as account numbers, credit information, account balances, and more.
According to the European Court of Justice (ECJ), your IP address is also considered personal data. IT experts can use your IP address to determine at least the approximate location of your device and, consequently, your location as the owner of the connection. Therefore, storing an IP address also requires a legal basis under the GDPR. There are also so-called “special categories” of personal data that are particularly worthy of protection. These include:
- racial and ethnic origin
- political views
- religious or ideological beliefs
- Union membership
- genetic data, such as data obtained from blood or saliva samples
- biometric data (this is information about psychological, physical, or behavioral characteristics that can identify an individual).
Health Data - Data relating to sexual orientation or sex life
Profiling
Definition pursuant to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“Profiling” means any form of automated processing of personal data that involves the use of personal data to evaluate certain personal aspects relating to a natural person, in particular to analyze or predict aspects concerning that natural person’s work performance, economic situation, health, personal preferences, interests, reliability, behavior, location, or movements;
Explanation: Profiling involves collecting various types of personal data about an individual in order to learn more about that person. On the internet, profiling is often used for advertising purposes or for credit checks. Web and advertising analytics programs, for example, collect data about your behavior and interests on a website. This results in a specific user profile that can be used to target advertisements to specific audiences.
Controller
Definition pursuant to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“controller” means the natural or legal person, public authority, agency, or other body that, alone or jointly with others, determines the purposes and means of the processing of personal data; where the purposes and means of such processing are determined by Union or Member State law, the controller or the specific criteria for its designation may be provided for by Union or Member State law;
Explanation: In our example, we are responsible for processing your personal data and are therefore the “controller.” If we share the data we have collected with other service providers for processing, they are considered “processors.” In such cases, a “Data Processing Agreement (DPA)” must be entered into.
Processing
Definition pursuant to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“processing” means any operation or set of operations performed on personal data or on sets of personal data, whether or not by automated means, such as collection, recording, organization, structuring, storage, adaptation or alteration, retrieval, consultation, use, disclosure by transmission, dissemination, or otherwise making available, alignment or combination, restriction, erasure, or destruction;
Note: When we refer to "processing" in our Privacy Policy, we mean any type of data processing. As mentioned above in the original GDPR statement, this includes not only the collection but also the storage and processing of data.
All texts are protected by copyright.